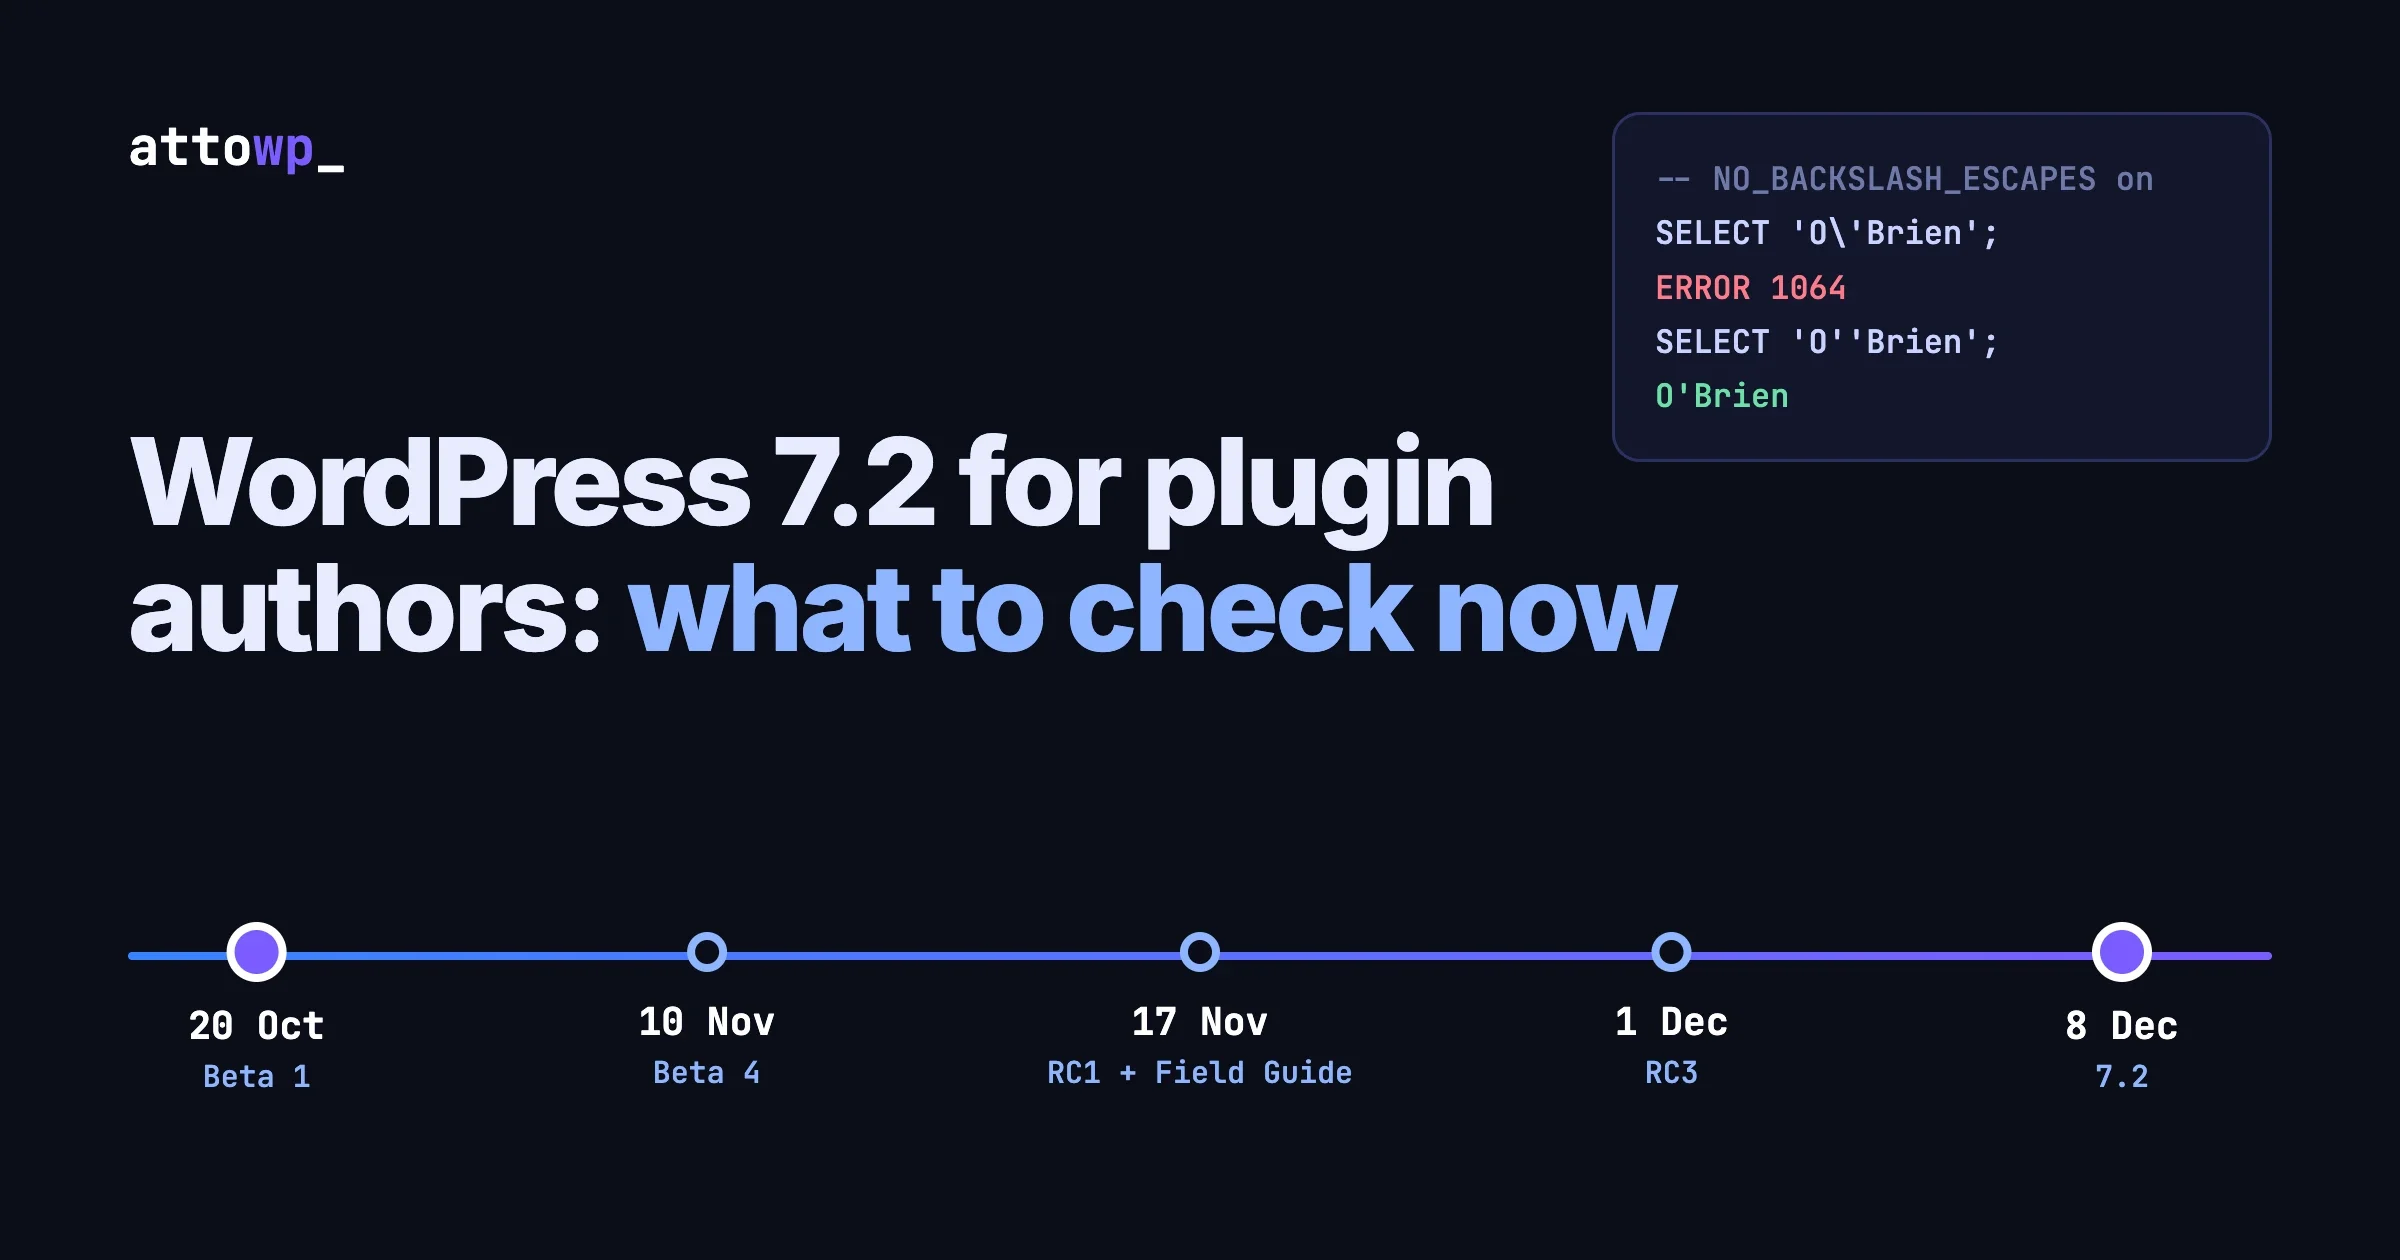
WordPress 7.2 for Plugin Authors: What to Check Now
WordPress 7.2 turns off the NO_BACKSLASH_ESCAPES SQL mode on its own connection. What it does (tested), which plugins to check, and the beta schedule.
WordPress 7.2 turns off the NO_BACKSLASH_ESCAPES SQL mode on its own connection. What it does (tested), which plugins to check, and the beta schedule.
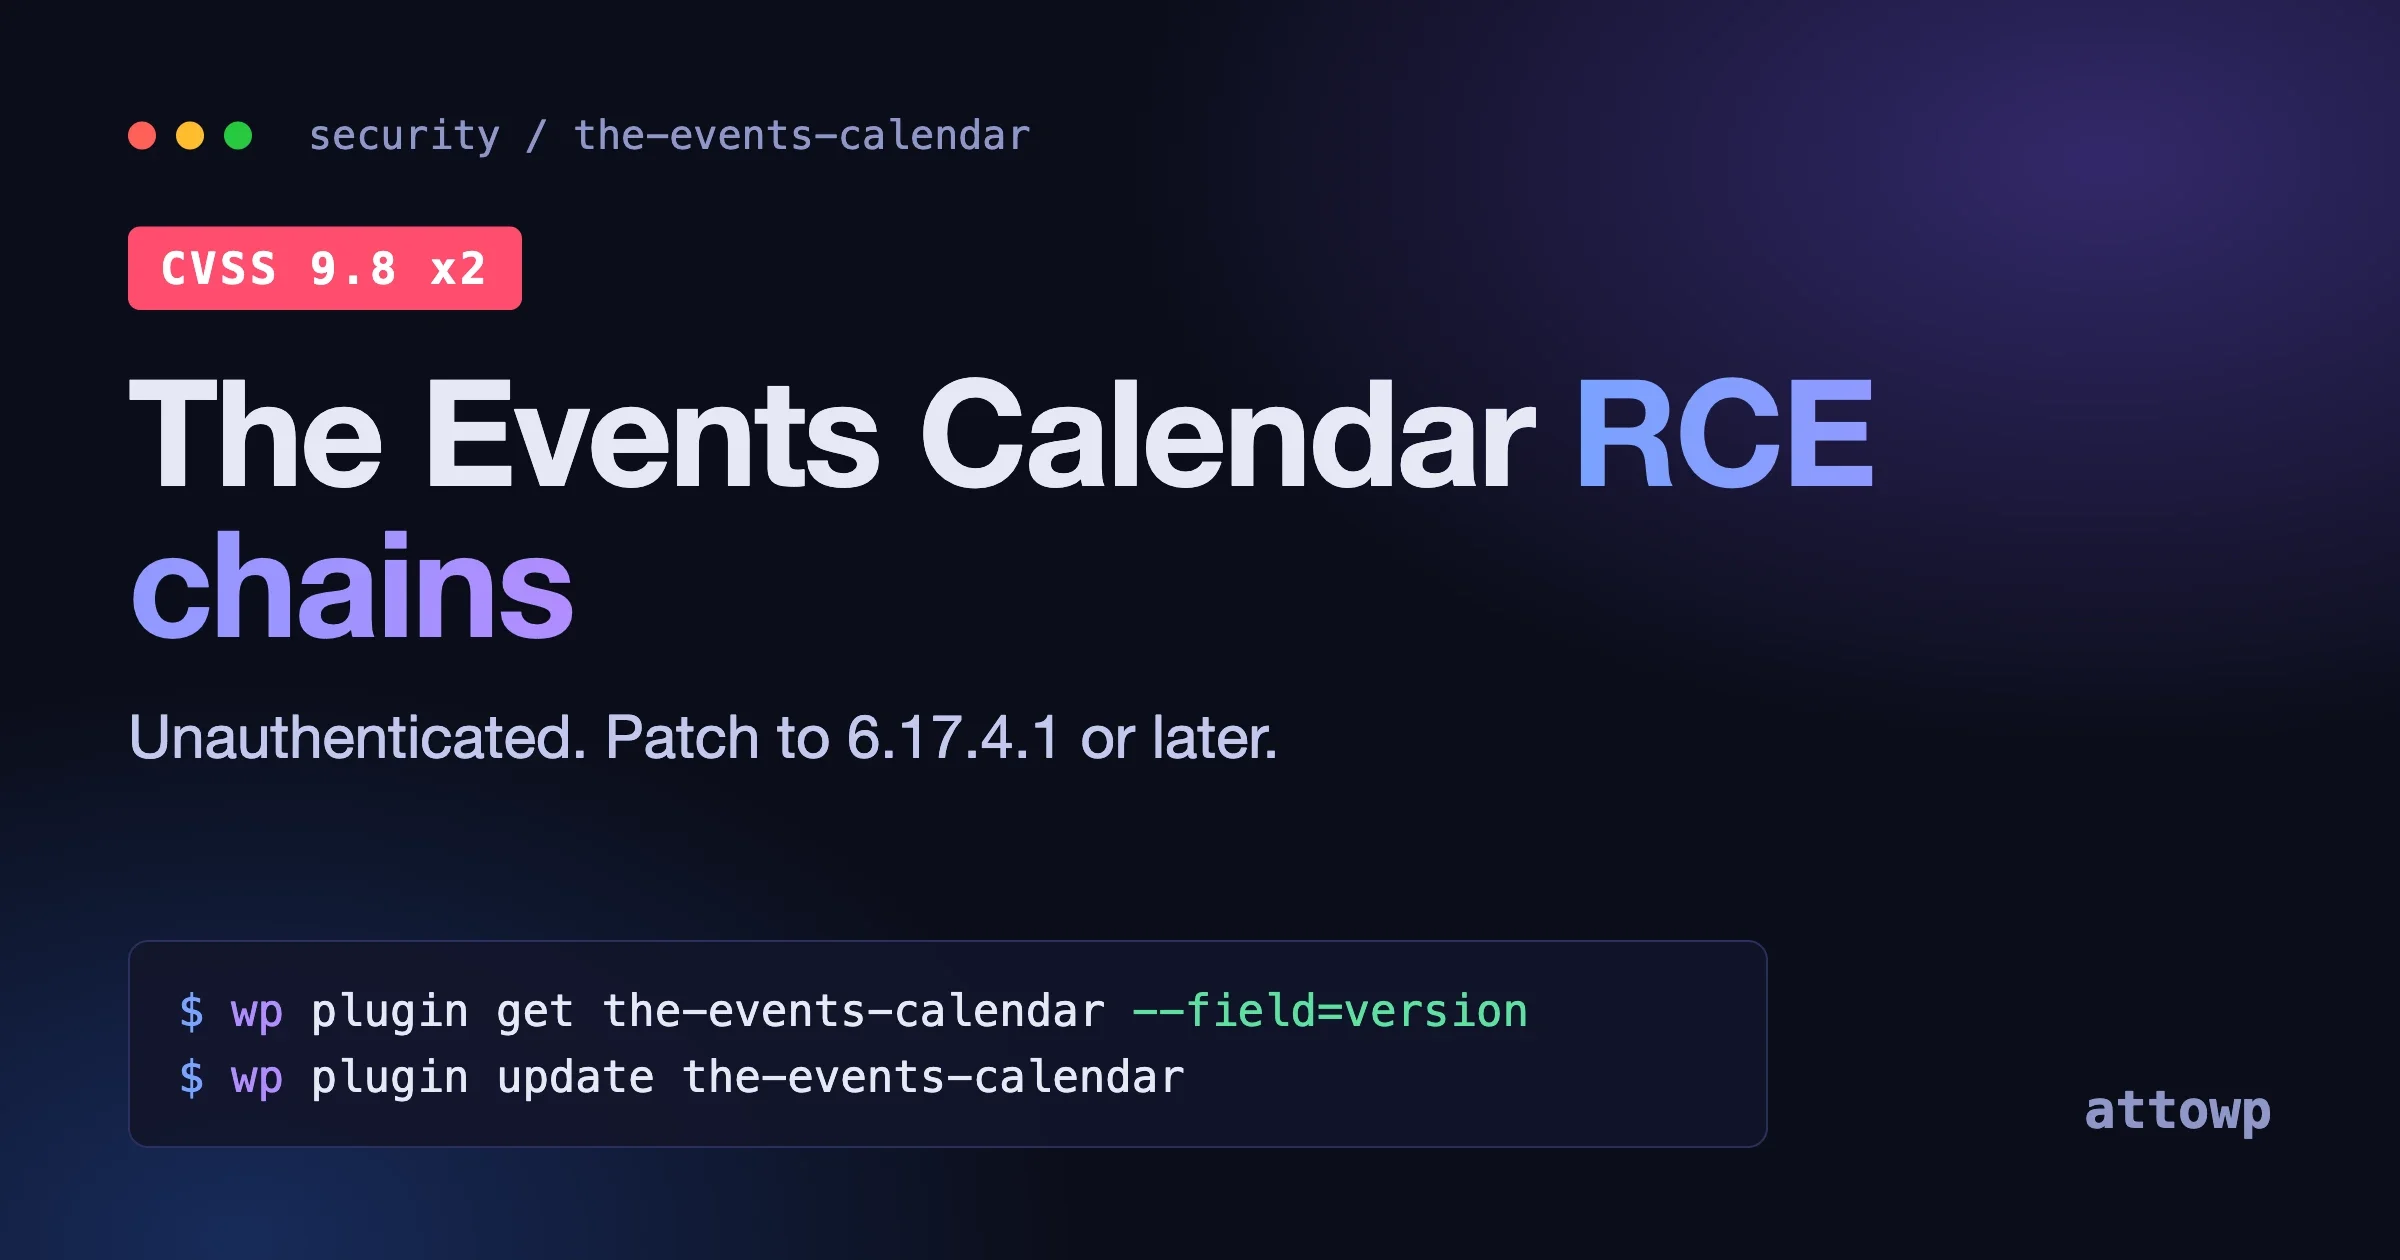
Two unauthenticated RCE chains in The Events Calendar (CVE-2026-78006 and CVE-2026-78159) start from an event comment. Who is exposed, WP-CLI checks for one site or a fleet, the patch, and what to hunt for.
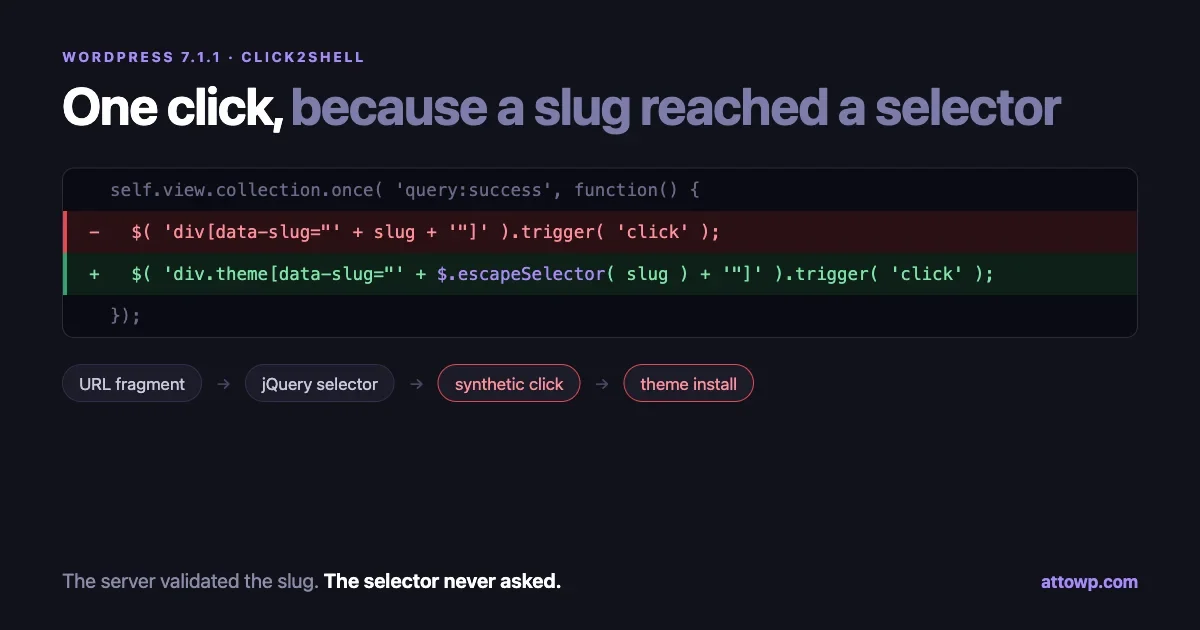
WordPress 7.1.1 fixed Click2Shell with two lines: escape a theme slug before it reaches a jQuery selector. Why server-side validation did not help, why the selector failed silently instead of throwing, and how to find the same shape in your own plugin JavaScript.
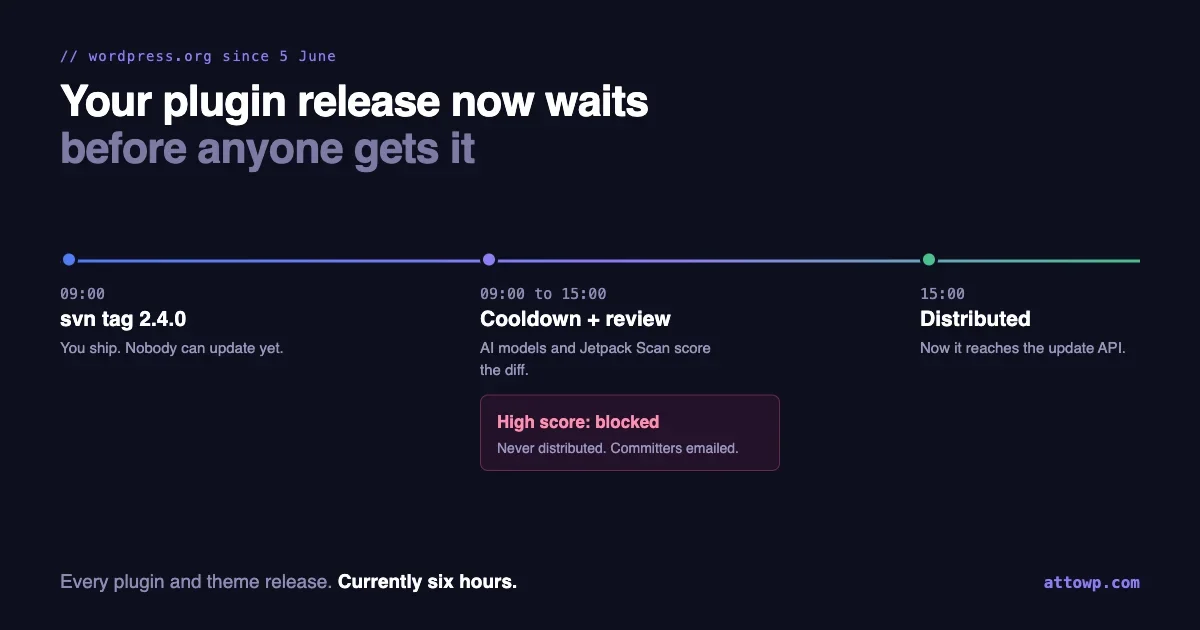
Since 5 June every plugin and theme release on WordPress.org waits in a cooldown, currently six hours, while AI models and Jetpack Scan review it. High-risk releases are blocked automatically. What that changes for announcing, hotfixing and shipping security fixes.
10 essential WordPress PHP snippets covering performance, security, and admin customization. Disable emojis, custom login URL, role-based redirects, limit login attempts, defer scripts, and more - all without plugins.
A practical WordPress security hardening checklist covering authentication, file permissions, login protection, database prefixes, and plugin hygiene - tested against current attack patterns.
WPCS MCP Server automates WordPress Coding Standards enforcement using AI. Save hours of manual PHPCS fixes with intelligent auto-correction for spacing, Yoda conditions, escaping, and docblocks. Open source tool for Claude Code and Claude Desktop.