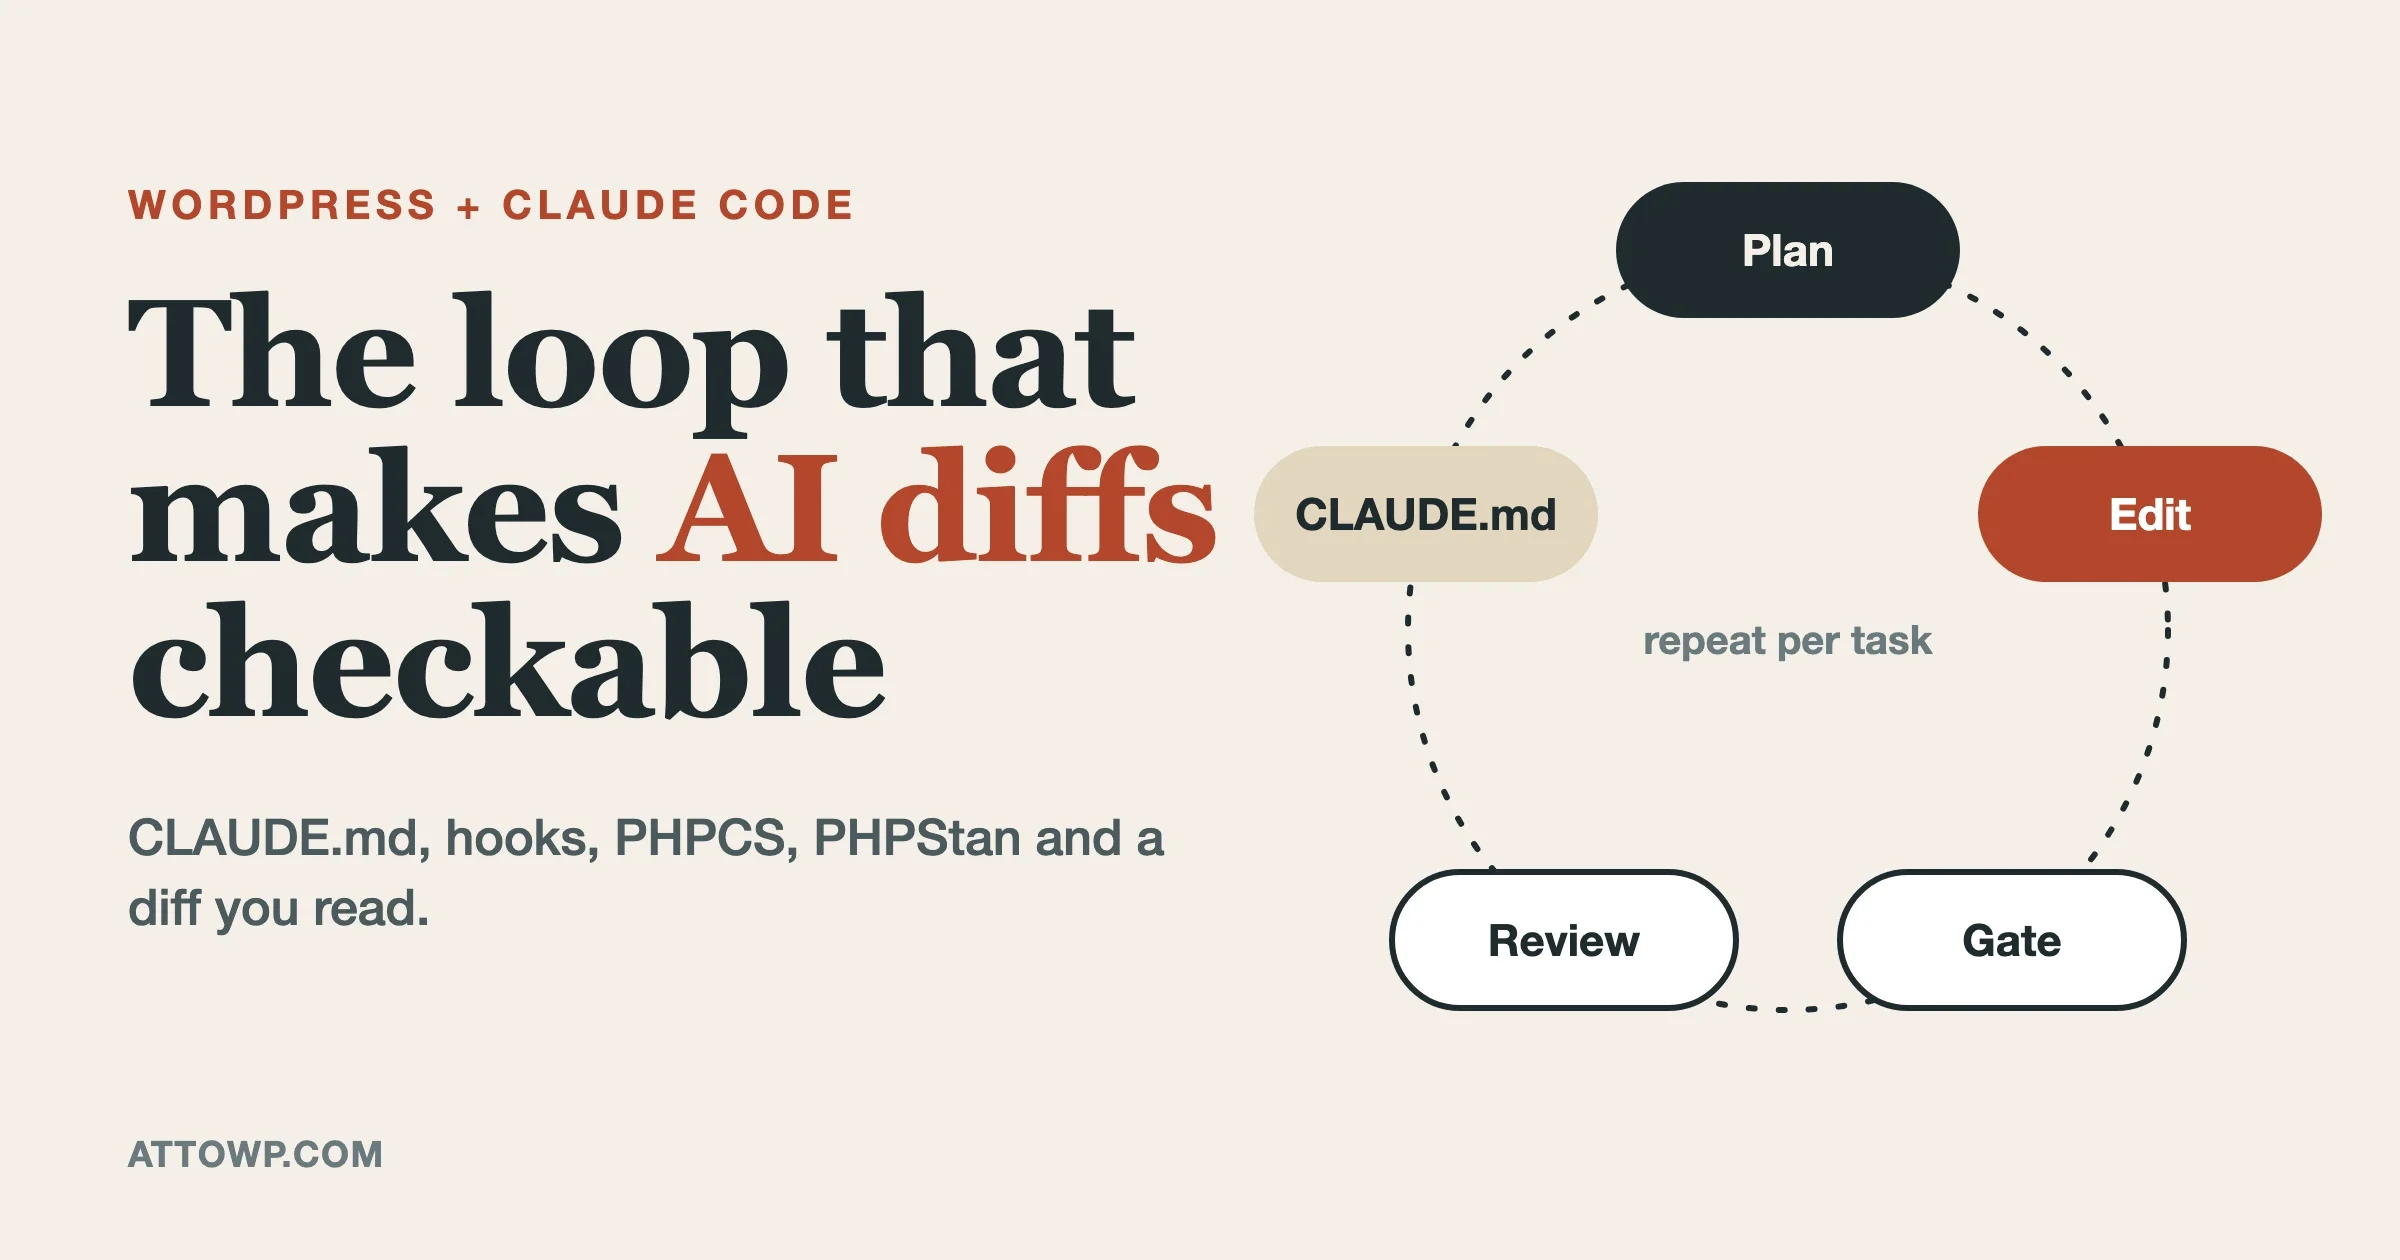
A workable Claude Code workflow for WordPress is a loop: put your rules in CLAUDE.md, plan in plan mode, let Claude make small edits against a local site, run PHPCS, PHPStan and your tests after every change, and read the diff yourself before anything is committed. The editing is the fast part. What decides whether the tool saves time is the setup that makes each diff checkable.
This guide walks through that setup in the order you would build it. We checked every Claude Code feature against Anthropic’s own documentation on 15 November 2026, and we ran the hook scripts, the PHPCS ruleset, the Composer scripts and the PHPStan config below on PHP 8.5.5 with WPCS 3.4.1 and PHPStan 2.3.5. We make no claim about anyone’s daily setup. Treat this as a method to try on one plugin and measure.
What does a Claude Code workflow for WordPress look like?
Five steps repeat for every task, and each one has a place where it lives so it does not depend on anyone remembering it.
Step | What happens | Where it lives |
|---|---|---|
1. Brief | You describe the task and the files involved. Claude reads the code and proposes a plan before touching anything. | Plan mode, started with |
2. Rules | Project conventions load at the start of every session. |
|
3. Edit | Claude changes files in small steps, against a local site, never a live one. | Local environment (Studio, Playground or wp-env) |
4. Gate | PHPCS, PHPStan, tests and Plugin Check run on every change. | Composer scripts, plus a hook so they run without being asked |
5. Review | You read the diff, try the feature in a browser and commit. | Your own review, plus an optional review subagent |
If you want a comparison of Claude Code against Cursor and Copilot before you commit to it, we keep that in a separate guide: Claude Code vs GitHub Copilot vs Cursor in 2026. This post assumes you already chose Claude Code and want a loop that holds up on real plugin code.
How do you set up a WordPress repo for Claude Code?
Start with three things that have nothing to do with AI: a Git repository, Composer scripts for every check, and a local site you can break. Claude Code can only work as well as the feedback it gets, and a plugin with no runnable checks gives it nothing to learn from.
Install Claude Code from the official overview page. The native installer is the recommended route on macOS, Linux and WSL (curl -fsSL https://claude.ai/install.sh | bash), and Homebrew offers brew install --cask claude-code. Then run claude inside the plugin folder. Run /init once to generate a starting CLAUDE.md from what Claude finds in the repo, then edit it by hand.
Next, wrap each check in a Composer script so the command is the same for you, for Claude Code and for CI. This is the composer.json we used (checked on 15 Nov 2026):
{
	"name": "acme/my-plugin",
	"type": "wordpress-plugin",
	"require": { "php": ">=8.1" },
	"require-dev": {
		"wp-coding-standards/wpcs": "^3.4",
		"phpcompatibility/phpcompatibility-wp": "^2.1",
		"dealerdirect/phpcodesniffer-composer-installer": "^1.0",
		"phpstan/phpstan": "^2.1",
		"szepeviktor/phpstan-wordpress": "^2.0",
		"phpstan/extension-installer": "^1.4",
		"yoast/phpunit-polyfills": "^4.0",
		"phpunit/phpunit": "^9.6 || ^10.5 || ^11.0"
	},
	"config": {
		"allow-plugins": {
			"dealerdirect/phpcodesniffer-composer-installer": true,
			"phpstan/extension-installer": true
		}
	},
	"scripts": {
		"lint": "phpcs",
		"analyse": "phpstan analyse --memory-limit=1G",
		"test": "phpunit",
		"check": ["@lint", "@analyse", "@test"]
	}
}
The dealerdirect/phpcodesniffer-composer-installer package registers WPCS with PHPCS, and phpstan/extension-installer loads the WordPress extension for PHPStan. Both need the allow-plugins entries shown, or Composer will refuse to run them.
Which local WordPress environment should Claude Code use?
Use one that is cheap to reset. Three options are common, and none of them needs production credentials.
Option | Runtime | Start it with | Good for |
|---|---|---|---|
Native PHP runtime and SQLite, no Docker. Desktop app plus a CLI. Latest release v2.2.0 (11 Nov 2026). |
| A full local site with a GUI, previews and a built-in MCP server for agents | |
WordPress in WebAssembly with SQLite. Needs Node.js 20.18 or higher. |
| Throwaway tests and demos. Auto-mounts the plugin, logs you in, takes | |
Docker containers (default), configured in |
| Repeatable team setups, PHPUnit against a real database, Xdebug |
For wp-env, run project tools from the plugin folder inside the container with --env-cwd:
# checked on 15 Nov 2026 against the wp-env README
npx @wordpress/env start
npx wp-env run cli --env-cwd=wp-content/plugins/my-plugin composer install
npx wp-env run cli --env-cwd=wp-content/plugins/my-plugin composer test
We covered how to connect an agent to Playground in Connect AI Coding Agents to WordPress Playground with MCP, so we will not repeat that setup here. WordPress.org currently recommends PHP 8.3 or higher, so pin your local environment to a version your plugin supports and test the oldest one too.
What belongs in CLAUDE.md for a WordPress plugin?
Put what Claude cannot work out by reading the code: the commands to run, the rules you enforce in review, and what “done” means. Anthropic’s memory documentation says to aim for under 200 lines per file, because longer files use more context and reduce how well instructions are followed. Directory layouts and dependency lists are better left out, since Claude can read them from the repo.
Where the file lives matters, and the docs list these locations:
File | Scope | Shared with the team? |
|---|---|---|
| This project | Yes, commit it |
| Your personal project preferences, such as local site URLs | No, add it to |
| All your projects | No |
| Rules scoped to file paths, loaded only when Claude works on matching files | Yes, commit it |
| Read by Claude Code in place of CLAUDE.md where the docs say it applies. See the AGENTS.md section of the memory docs for the exact rules | Yes |
Here is a CLAUDE.md for a small plugin. It is 25 lines, and every rule in it maps to something a reviewer would otherwise write in a pull request comment:
# My Plugin

WordPress plugin. Requires WordPress 6.6+, PHP 8.1+. Main file: my-plugin.php.

## Layout
- includes/ : classes, one per file, namespace MyPlugin
- src/js/ : block and admin scripts, built with `npm run build` into build/
- tests/ : PHPUnit tests (WP test suite)

## Commands
- `composer lint` : PHPCS with WordPress-Extra (phpcs.xml.dist)
- `composer analyse` : PHPStan level 5 with szepeviktor/phpstan-wordpress
- `composer test` : PHPUnit
- Local site: `npx wp-env start`, WP-CLI via `npx wp-env run cli wp ...`

## Rules
- Every REST route has a real permission_callback. Never `__return_true` on a write.
- Sanitize on input, escape on output, nonce plus capability check on every form and AJAX handler.
- Database access through $wpdb->prepare(). No raw SQL strings with variables.
- All strings use the text domain `my-plugin`.
- Do not edit build/ or vendor/ by hand.
- Never run WP-CLI against a remote site or an alias. Local wp-env only.

## Done means
composer lint, composer analyse and composer test pass, and the change was tried in the browser.
One honest limit: CLAUDE.md is delivered to the model as context, not enforced. The docs say there is no guarantee of strict compliance, especially for vague or conflicting instructions. Anything that must happen every time belongs in a hook, which the next sections cover.
Which permission mode should you use for WordPress work?
Pick the mode by how much of the diff you plan to read. The permission modes page lists six modes, and you switch between them with Shift+Tab in the CLI.
Mode | Runs without asking | Fits WordPress work like |
|---|---|---|
| Reads only | Unfamiliar code, anything near payments or user data |
| Reads, no edits until you approve a plan | The first pass on any task, or learning a plugin you did not write |
| Reads, file edits and basic filesystem commands | Iterating on a change you are reviewing live |
| Everything, with a second model checking each action | Long tasks inside a disposable local environment |
| Only pre-approved tools; everything else is denied | CI scripts with an exact allowlist |
| Everything | Containers and VMs only |
With Claude Code v2.1.283 or later, auto mode is the built-in starting mode for interactive terminal and VS Code sessions, so check which mode your session started in before you assume Claude will ask first. Anthropic’s own warning on auto mode is worth repeating: it reduces prompts but does not guarantee safety, so use it where you trust the general direction of the task.
A practical default for plugin work is plan mode for the first pass, then acceptEdits while you read each change, with deny rules covering the commands you never want run. Deny rules apply in every mode, including bypassPermissions. Here is a project .claude/settings.json that does that and wires in the two hooks from the next section:
{
  "permissions": {
    "allow": [
      "Bash(composer lint)",
      "Bash(composer analyse)",
      "Bash(composer test)",
      "Bash(git diff *)",
      "Bash(git status *)"
    ],
    "deny": [
      "Bash(git push *)",
      "Bash(wp db reset *)",
      "Read(./.env)",
      "Read(./wp-config.php)"
    ]
  },
  "hooks": {
    "PreToolUse": [
      {
        "matcher": "Bash",
        "hooks": [
          {
            "type": "command",
            "command": "${CLAUDE_PROJECT_DIR}/.claude/hooks/block-live-wp.sh"
          }
        ]
      }
    ],
    "PostToolUse": [
      {
        "matcher": "Edit|Write",
        "hooks": [
          {
            "type": "command",
            "command": "${CLAUDE_PROJECT_DIR}/.claude/hooks/phpcs-after-edit.sh"
          }
        ]
      }
    ]
  }
}
Rule syntax follows the permissions reference: Bash(composer lint) matches that exact command, and a trailing * after a space matches any arguments. A deny rule always beats an allow rule, so you cannot carve an exception out of a broad deny.
How do hooks enforce WordPress rules?
A hook is a shell command Claude Code runs at a fixed point, such as before a tool call or after a file edit. It runs whether or not Claude remembers your rule. Exit code 2 from a PreToolUse hook blocks the action, and exit code 2 from a PostToolUse hook sends your stderr to Claude so it can fix what it just wrote. The hooks reference covers every event. Two hooks do most of the work for a plugin.
Run PHPCS after every PHP edit
This script reads the edited file path from the hook input and lints only that file. When PHPCS fails, the output goes back to Claude and it corrects the file in the same turn:
#!/bin/bash
# PostToolUse hook: lint PHP files Claude just edited. Exit 2 shows stderr to Claude.
FILE=$(jq -r '.tool_input.file_path // empty')
case "$FILE" in
  *.php) ;;
  *) exit 0 ;;
esac

OUT=$("${CLAUDE_PROJECT_DIR}/vendor/bin/phpcs" --standard="${CLAUDE_PROJECT_DIR}/phpcs.xml.dist" "$FILE" 2>&1) || {
  echo "$OUT" >&2
  exit 2
}
We fed it a file with an unescaped $_GET value and a missing doc comment. It exited with code 2 and printed seven findings, including WordPress.Security.EscapeOutput.OutputNotEscaped. On a clean file it exited 0 and printed nothing.
Block WP-CLI against a remote site
WP-CLI can reach a remote site through --ssh=, --http= or an alias such as @production. This hook denies any such command. It will not stop a determined mistake, because a shell command can be written many ways, but it catches the common ones and tells Claude why:
#!/bin/bash
# PreToolUse hook: stop WP-CLI from reaching a remote or aliased site.
COMMAND=$(jq -r '.tool_input.command')

if echo "$COMMAND" | grep -Eq 'wp( [^|;&]*)? (@[a-z0-9_-]+|--ssh=|--http=)'; then
  jq -n '{
    hookSpecificOutput: {
      hookEventName: "PreToolUse",
      permissionDecision: "deny",
      permissionDecisionReason: "WP-CLI against a remote or aliased site is blocked. Run it locally."
    }
  }'
else
  exit 0
fi
We tested four commands: wp @production option get siteurl and wp plugin list --ssh=u@h were denied, while wp option get siteurl and wp plugin list passed. Remember to run chmod +x on both scripts, and install jq, which both use to read the JSON input.
When do skills and subagents help?
Use them to keep long procedures and noisy research out of CLAUDE.md. A skill is a folder with a SKILL.md whose body loads only when it is used, so a long checklist costs almost nothing until you need it. A subagent runs in its own context window with its own tool access, which keeps big searches out of your main conversation. Here is where each one fits:
You need | Use | Why |
|---|---|---|
A fact every session needs, such as the test command |
| Loads every session |
A rule that must run every time | Hook | Runs regardless of what Claude decides |
A procedure you paste often, such as a release checklist | Skill | Body loads only when invoked |
Rules that apply to one folder or file type |
| Loads only on matching files |
A second opinion on a diff, or a wide code search | Subagent | Separate context, restricted tools |
Access to an outside system such as GitHub or a database | MCP server | Adds tools, not instructions |
A release-check skill
Skills live in .claude/skills/<name>/SKILL.md for a project, or ~/.claude/skills/ for all your projects. Setting disable-model-invocation: true means Claude will not run it on its own; you invoke it with /release-check. See the skills documentation for the full frontmatter list.
---
name: release-check
description: Pre-release checklist for this plugin. Run before tagging.
disable-model-invocation: true
---

Before a release:

1. Run `composer lint`, `composer analyse` and `composer test`. Stop on any failure.
2. Run `npx wp-env run cli wp plugin check my-plugin` (the Plugin Check plugin must be active).
3. Confirm the version in my-plugin.php, readme.txt and package.json match.
4. List every `_doing_it_wrong` or deprecation notice in the debug log.
5. Summarise what changed since the last git tag, grouped as New, Improve, Fix.
A review subagent
Claude Code also ships built-in subagents. Explore is a read-only agent for searching and analysing a codebase, and Plan is the research agent used in plan mode; both are denied Write and Edit. A custom subagent goes in .claude/agents/. This one reviews a diff and cannot edit anything, because its tool list has no Write or Edit:
---
name: wp-reviewer
description: Reviews a WordPress plugin diff for security, escaping, i18n and hook mistakes. Use after any change to PHP files.
tools: Read, Grep, Glob, Bash
model: sonnet
---

You review WordPress plugin code. Run `git diff` first, then check each changed
file for: missing nonce or capability checks, unsanitized input, unescaped
output, queries without $wpdb->prepare(), REST routes without a real
permission_callback, and strings outside the text domain. Report findings as
file:line with a one-line fix. Do not edit files.
Anthropic documents the file format in the subagents reference. A reviewing subagent is a second pass, not a replacement for your own read of the diff.
WordPress agent skills
The WordPress project publishes a WordPress/agent-skills repository with skills for blocks, block themes, plugin development, the REST API, the Interactivity API, WP-CLI, performance, PHPStan, Playground and wp-env. Its README installs them with npx skills add WordPress/agent-skills --skill wp-plugin-development, and adding --global installs to your home directory instead of the project. The README also discloses that the skills were generated with an AI model from official Gutenberg and WordPress documentation and then reviewed by contributors, and calls itself v1. Read a skill before you rely on it, as you would a dependency.
How do MCP servers and scopes fit in?
MCP servers give Claude Code tools it does not have by default, such as GitHub, a browser or a WordPress site. They are the one place where an agent can reach outside your repo, so scope them deliberately. The MCP documentation defines three installation scopes:
Scope | Loads in | Shared with the team? | Stored in |
|---|---|---|---|
Local (the default) | The current project only | No |
|
Project | The current project only | Yes, through version control |
|
User | All your projects | No |
|
When the same server name exists in more than one place, local wins over project, and project wins over user. Claude Code asks for approval before using a server from a project’s .mcp.json in interactive sessions, which matters when you clone a repository you did not write.
# checked on 15 Nov 2026 against the Claude Code MCP docs
# Personal, this project only (local scope is the default)
claude mcp add --transport http stripe https://mcp.stripe.com

# Shared with everyone who clones the repo
claude mcp add --transport http shared-server --scope project https://example.com/mcp

# Available in every project on this machine
claude mcp add --transport http hubspot --scope user https://mcp.hubspot.com/anthropic
For WordPress, the useful servers fall into two groups: the ones that run your site (the official WordPress MCP Adapter, the Studio MCP server) and the ones around it (GitHub, a browser). We compare the ways to connect an agent to a site in MCP tools with Codex and Claude: setup and use cases and show the WP-CLI side in WP-CLI commands worth knowing, and how AI agents use them. Give an MCP server a read-only account first. A server that can publish posts or change options is a write path into your site, whatever tool is calling it.
Which checks should every diff pass?
Every change should pass the same four automated gates, in this order, before a person reads it. Each gate catches a different kind of mistake, and none of them replaces the others.
Gate | Command | Catches |
|---|---|---|
| Escaping, nonce and sanitization patterns, i18n, doc comments, PHP version compatibility | |
| Wrong types, undefined methods, bad return values, wrong WordPress function arguments | |
PHPUnit |
| Behaviour: does the code still do what the tests say |
| WordPress.org directory rules, security and performance checks. Version 2.2.0 released 6 Nov 2026 |
The PHPCS ruleset we used pulls in WordPress-Extra and WordPress-Docs for style and security patterns, and PHPCompatibilityWP for PHP version compatibility. The testVersion value 8.1- checks the code against PHP 8.1 and every newer version, and minimum_wp_version tells WPCS the oldest WordPress you support so it can flag functions deprecated by then:
<?xml version="1.0"?>
<ruleset name="My Plugin">
	<description>Coding standards for My Plugin.</description>

	<file>.</file>
	<exclude-pattern>*/vendor/*</exclude-pattern>
	<exclude-pattern>*/node_modules/*</exclude-pattern>

	<arg name="extensions" value="php"/>
	<arg value="ps"/>

	<rule ref="WordPress-Extra"/>
	<rule ref="WordPress-Docs"/>
	<rule ref="PHPCompatibilityWP"/>

	<config name="testVersion" value="8.1-"/>
	<config name="minimum_wp_version" value="6.6"/>

	<rule ref="WordPress.WP.I18n">
		<properties>
			<property name="text_domain" type="array">
				<element value="my-plugin"/>
			</property>
		</properties>
	</rule>
</ruleset>
PHPStan needs only a short config. The phpstan-wordpress extension brings WordPress function stubs, so calls such as get_option() and register_rest_route() are typed. Start at a level you can pass and raise it over time; level 5 was clean on the example plugin below.
parameters:
	level: 5
	paths:
		- my-plugin.php
Plugin Check needs the Plugin Check plugin active in the site. Its README notes that WP-CLI runs only the static checks by default, and runtime checks need an extra --require argument. A failing gate is useful information for Claude. Paste the output back, or let the hook do it, and ask for the smallest fix. Do not accept a change that silences a sniff with an ignore comment unless you can say why the sniff is wrong for that line.
How do you review what Claude changed?
Read the diff the way you would read a new contributor’s pull request, with extra attention on the places where a plausible-looking WordPress API call is wrong. Use git diff or your editor’s diff view, and stage hunk by hunk with git add -p so nothing goes in unread. These are the checks a scanner cannot do for you:
Look for | Why it matters | What correct looks like |
|---|---|---|
A write route or AJAX handler with no capability check | Any visitor can call it |
|
A nonce check that verifies the wrong action | The check exists but protects nothing |
|
Input used directly | Stored or reflected content can carry markup | A sanitizer such as |
SQL built with string concatenation | SQL injection |
|
Hooks added at the wrong priority or in the wrong context | Code runs too early, too late, or on the front end only | Check against the hook reference on developer.wordpress.org |
A function that does not exist in your minimum WordPress version | Fatal error on older sites | Check the “Changelog” table on the function’s reference page |
Here is a small REST endpoint that passes every gate above. PHPCS reports no violations with the ruleset shown, PHPStan level 5 reports no errors, and php -l finds no syntax errors. The two details a reviewer should look for are the permission_callback and the sanitizer on the argument:
<?php
/**
 * Plugin Name: My Plugin
 * Text Domain: my-plugin
 *
 * @package MyPlugin
 */

namespace MyPlugin;

add_action( 'rest_api_init', __NAMESPACE__ . '\register_routes' );

/**
 * Register the REST routes.
 *
 * @return void
 */
function register_routes() {
	register_rest_route(
		'my-plugin/v1',
		'/settings',
		array(
			'methods'             => 'POST',
			'callback'            => __NAMESPACE__ . '\save_settings',
			'permission_callback' => static function () {
				return current_user_can( 'manage_options' );
			},
			'args'                => array(
				'label' => array(
					'type'              => 'string',
					'required'          => true,
					'sanitize_callback' => 'sanitize_text_field',
				),
			),
		)
	);
}

/**
 * Save the settings.
 *
 * @param \WP_REST_Request $request The request.
 * @return \WP_REST_Response
 */
function save_settings( \WP_REST_Request $request ) {
	update_option( 'my_plugin_label', $request->get_param( 'label' ) );

	return rest_ensure_response( array( 'saved' => true ) );
}
Passing gates still does not mean the feature works. Open the plugin in your local site, try the happy path and one failure path, and check the browser console and the PHP error log. For admin screens, check a narrow viewport as well. Claude Code can drive a browser through an MCP server, but a human glance at the result is cheap and catches layout problems no linter sees.
Is it safe to use Claude Code on a live WordPress site?
Do not point it at one. Develop locally, push through Git, and deploy with your normal process. The risks are practical rather than exotic: a command run against the wrong environment, a secret read into a prompt, or content from the web treated as an instruction.
- Keep credentials out of reach. Add
Read(./.env)andRead(./wp-config.php)deny rules, as in the settings above. Use a local database with throwaway data, not a copy of production customer records. - Separate write access. Deny
git pushso a person pushes. Block remote WP-CLI with the hook above. Give any MCP server the lowest account role that works. - Treat fetched content as untrusted. A web page, a support ticket or a post body can contain text written to steer an agent. Anthropic describes auto mode’s classifier as blocking actions that look driven by hostile content Claude read, but treat that as a backstop, not a plan.
- Review third-party code the same way. A WordPress.org or GitHub skill, plugin or MCP server runs with the access you give it.
For security-sensitive code, use the gates and your own read of every authentication, payment and data-export path. The WordPress security handbook covers nonces, capability checks, sanitizing and escaping, and it is the reference to review against.
What does Claude Code cost for WordPress work?
Claude Code is included in every paid Claude plan and shares the same usage limits as chat. Prices below are from claude.com/pricing, checked on 15 November 2026, and exclude tax. Plans and prices can change.
Plan | Price | Claude Code | Usage |
|---|---|---|---|
Free | $0 | Not included | Limited |
Pro | $17 a month on an annual plan ($200 billed up front), or $20 billed monthly | Included | More than Free, reset every 5 hours with weekly limits |
Max | $100 a month | Included | 5x Pro usage, every 5 hours and every week |
Ultra | $200 a month | Included | 10x Pro usage every week, no 5-hour limit for verified accounts |
Team, standard seat | $20 per seat a month annually, $25 monthly | Included | More than Pro |
Team, premium seat | $100 per seat a month annually, $125 monthly | Included | 5x a standard seat |
Enterprise | $20 per seat a month plus usage at API rates | Included | Billed on usage |
For heavy sessions you can switch to pay-as-you-go API credits through a Console account instead. Costs rise with the amount of code Claude reads, so three habits help: name the files you want looked at, keep CLAUDE.md short and specific, and start a fresh session when the task changes. The usage meter in your account settings is the source of truth, so measure one real task before you plan a budget around a plan.
Common mistakes people report
We looked for recurring problems in the Claude Code issue tracker on GitHub, in WordPress’s own agent-skills README and in Anthropic’s troubleshooting notes. Reddit was not reachable from our research setup on 15 November 2026, so none of these come from it. Checked on 15 November 2026.
- Treating CLAUDE.md as enforcement. Several open reports describe rules in CLAUDE.md being skipped, for example issue 2544 and issue 33603. Anthropic’s memory docs say the same thing in milder words: there is no guarantee of strict compliance. Fix: move must-run rules into a hook or a deny rule.
- Letting CLAUDE.md grow past what is useful. The docs warn that files over 200 lines use more context and may reduce adherence, and Claude Code shows a warning at startup for oversized files. Fix: keep commands and non-obvious rules, and move folder-specific rules into
.claude/rules/. - Expecting outdated WordPress patterns to be fixed by the model alone. The WordPress agent-skills README says AI assistants often generate outdated patterns, miss security considerations and skip block deprecations, which is the reason that repository exists. Fix: run the gates, and give the agent current references.
- Hitting refusals on security-adjacent WordPress work. Two open reports describe it: a login-form request being refused and a malware-analysis task on a WordPress exploit being blocked. These are single reports and Anthropic has not confirmed either as a bug. Fix: reword the task around what you are building or defending, and keep a manual route for incident work.
- Running unattended in a mode with no checkpoints. Anthropic says auto mode does not guarantee safety. Fix: plan first, review hunks, and keep deny rules for pushes and remote commands.
When is Claude Code the wrong tool?
It is a poor fit when you cannot run the code, cannot define “correct”, or cannot read the result. A plugin with no tests and no staging site gives it no feedback, and a change to payment, authentication or personal data deserves your full attention regardless of the tool. Quick inline completions while you type are a different job, and an editor-based tool may suit that better; we compare them in our tools comparison and list more options in best AI tools for WordPress development.
It also does not replace knowing WordPress. If you cannot tell a nonce check from a capability check, you will not spot the mistake in the diff. Use the tool to move faster through work you already understand, and use the gates to catch what you miss.
A 30-minute trial
- Pick one plugin with a Git history and a local environment. Run
composer lintand note the baseline. - Run
/init, then cut the result to the commands and rules a reviewer would care about. - Add the two hooks and the deny rules from this guide.
- Start in plan mode and ask for a small change, such as a new filter or a settings field. Approve the plan, then switch to
acceptEdits. - Read the diff with the checklist above. Count how many findings the gates caught and how many you caught by reading.
That count tells you more than any benchmark. If the gates catch most problems and the diffs are small, the workflow fits. If you keep finding the same mistake, add it to CLAUDE.md or write a hook for it.
Frequently asked questions
Do I need a CLAUDE.md for WordPress?
No, Claude Code works without one, but every session then starts without your commands and rules. A short file with your test commands and your security rules is the cheapest improvement you can make. Keep it under about 200 lines.
Can Claude Code run WP-CLI?
Yes, it runs shell commands, so any command on your PATH works. Allow the safe read commands, deny anything destructive, and block remote targets with a hook. Our guide to WP-CLI commands for AI agents has a tested read-only wrapper.
Does Claude Code work with WordPress Studio and Playground?
Yes. Both can be driven from the terminal, and Studio documents a built-in MCP server for compatible agents including Claude Code. Playground runs from npx @wp-playground/cli@latest start.
Is Claude Code free?
No. The Free plan does not include it. It is included from Pro at $17 a month on an annual plan, or $20 billed monthly, as of 15 November 2026. You can also pay as you go through a Console account.
No comments yet