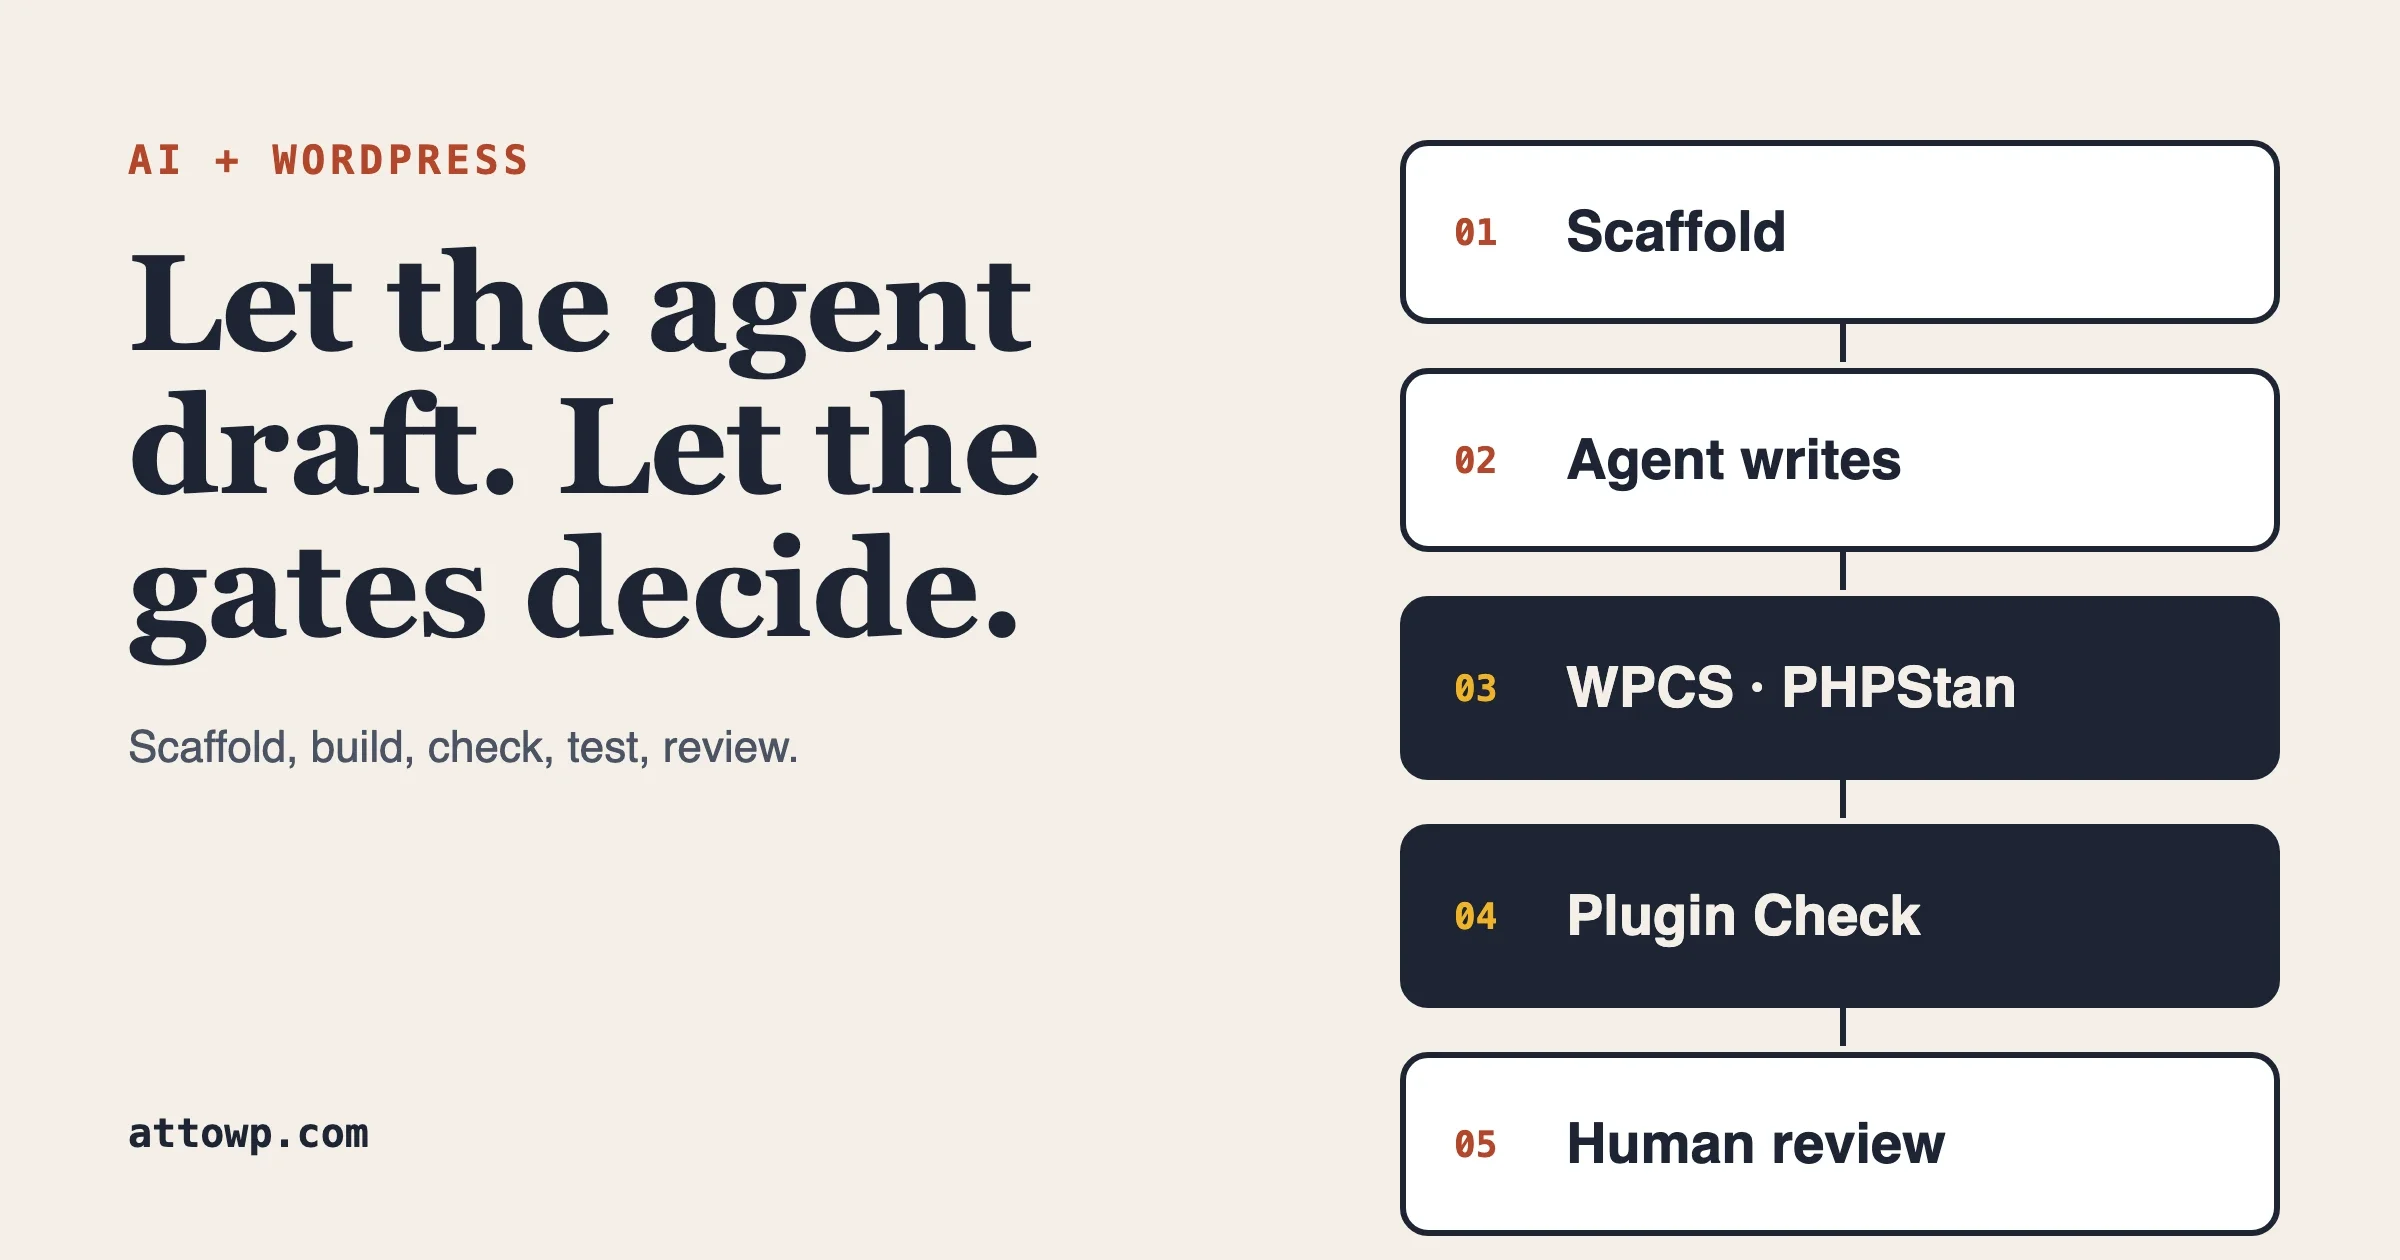
To automate WordPress theme and plugin development with AI, scaffold the project with official tools first, let an AI agent fill in the code in small reviewed steps, and run the result through coding standards, static analysis, Plugin Check and tests before anything ships. The agent writes the first draft. Your gates decide whether it is good. We checked every tool, model name and command below on 15 November 2026 against vendor and WordPress.org documentation.
One question still brings readers here from search: which Claude model for WordPress work. Claude 3.5 Sonnet, the model this article originally named, is no longer on Anthropic’s current models list. The current lineup is Claude Fable 5.2, Opus 5.5, Sonnet 5.5 and Haiku 5.5, covered in the next section. The rest of the article is about the workflow, because the workflow outlasts any model name.
Is Claude 3.5 Sonnet still the model to use for WordPress development?
No. Anthropic’s models overview, which we read on 15 November 2026, lists four current models and does not include Claude 3.5 Sonnet in its table of all models. Older models in the same family, such as Opus 4.5 and Sonnet 4.5, still appear there with their own pricing, so the 3.x line is the part that has dropped out of the list. If a tutorial tells you to pass a 3.5 model ID to the API, check the page below before copying it.
Model | API ID | Anthropic’s description | Price per million tokens (input / output) |
|---|---|---|---|
Claude Fable 5.2 |
| Demanding reasoning and long-horizon agentic work | $8 / $40 |
Claude Opus 5.5 |
| Long-running agentic coding and knowledge work | $4 / $20 |
Claude Sonnet 5.5 |
| Best combination of speed and intelligence | $2 / $10 |
Claude Haiku 5.5 |
| High-volume, latency-sensitive tasks such as classification and routing | From $0.10 / $0.50 |
Source: Anthropic models overview, checked 15 November 2026. All four list a 1M-token context window and 128K maximum output.
How should a WordPress developer read that table? Anthropic says to start with Opus 5.5 for most workloads and to move to Fable 5.2 when your own tests on Opus still fall short. For day-to-day plugin work that means a mid-priced model for scaffolding and refactors, and a cheaper one for chores like writing docblocks or classifying support tickets. Pricing and defaults change, so treat the table as a dated snapshot and re-read the source before you budget a project.
We have not benchmarked these models on WordPress tasks, and we will not claim one writes better PHP than another. The honest test is your own repository: run the same task on two models, then run the same gates on both outputs. For tool-by-tool comparisons across vendors, read our Claude Code, Copilot and Cursor compared and our best AI tools for WordPress development instead of repeating them here.
What can AI actually automate in theme and plugin development?
AI is good at the parts of WordPress development that follow a known shape. It is unreliable where the answer depends on your site, your users or your threat model. Splitting the work along that line is the single most useful habit we can recommend.
Task | Safe to hand to an agent? | Why |
|---|---|---|
Boilerplate: plugin header, main file, uninstall routine | Yes, then review | Fixed structure, easy to diff against the handbook |
| Yes, then validate | Schema-driven, errors show up in the editor quickly |
Unit tests for pure functions | Yes | Tests fail loudly if the logic is wrong |
Docblocks, README, inline comments | Yes | Low risk, but check every claim against the code |
Database schema and migrations | Draft only | A wrong index or missing upgrade path hurts live sites |
Anything touching authentication, payments or file uploads | Human-written, AI-reviewed | Mistakes become vulnerabilities, not bugs |
Architecture and data model decisions | Human decision | The agent cannot know your growth path |
Performance tuning | Measure first | Needs profiling on real data, not guesses |
Automation here means fewer keystrokes on repeatable work, not fewer decisions. We have seen no credible public measurement that gives a single productivity number for this, so we do not quote one. Track your own cycle time on a few real tickets before you promise a client anything.
How do you scaffold a plugin or block before the AI writes code?
Scaffold with official generators first, then ask the agent to extend what exists. Starting from a generator gives the agent real file names, real naming conventions and a working baseline, which cuts down on invented structure. It also gives you a clean first commit to diff against.
Plugin and test scaffolding with WP-CLI
WP-CLI’s scaffold family covers a plugin skeleton, a custom post type, a taxonomy and PHPUnit files. The command reference lists plugin, plugin-tests, theme-tests, post-type, taxonomy, child-theme, block and underscores. There is no plain theme subcommand, so classic starter themes come from wp scaffold _s.
# checked on 15 Nov 2026
wp scaffold plugin acme-orders --plugin_name="Acme Orders"
wp scaffold plugin-tests acme-orders --ci=github
wp scaffold post-type order --plugin=acme-orders
wp scaffold child-theme acme-child --parent_theme=twentytwentyfive
wp scaffold plugin-tests writes phpunit.xml.dist, bin/install-wp-tests.sh, tests/bootstrap.php, a sample test, .phpcs.xml.dist and a CI file. The --ci option accepts circle (the default), gitlab, bitbucket and github. Pick the one you use, because the agent will copy whatever it finds. Confirm the exact theme slug you pass to --parent_theme exists on your install before you run the child theme line.
Blocks with @wordpress/create-block
For blocks, the block editor handbook documents @wordpress/create-block and requires Node.js 22.13.0 or newer. The generated plugin still has to be installed in WordPress manually.
# checked on 15 Nov 2026
npx @wordpress/create-block@latest acme-callout
cd acme-callout
npm start

# dynamic block (server-rendered) from the built-in template
npx @wordpress/create-block@latest acme-latest --variant dynamic
The --template option takes standard (the default), es5, an npm package name or a local directory. If your agency has a house block template, put it in a package and point the agent at it. That one file does more to keep AI output consistent than any prompt.
Verify the scaffold before you prompt
- Activate the plugin on a throwaway site and confirm there are no PHP notices.
- Run
php -lon every PHP file the generator and the agent touch. - Commit the untouched scaffold, so every later AI change shows up as a clean diff.
- Write down the conventions in a short instructions file: text domain, function prefix, minimum PHP and WordPress versions, the test command.
How do AI agents work with WordPress Studio, Playground and MCP?
Agents become useful for WordPress when they can run the code they write. Three official routes exist today: WordPress Studio for local sites, WordPress Playground for disposable instances, and the WordPress.org MCP server for the plugin directory. MCP is the open protocol that lets an agent call tools such as “create a site” or “validate this readme”. If MCP is new to you, our explainer on how AI agents connect to external tools covers the model, and connecting coding agents to WordPress Playground goes deeper on that one setup.
WordPress Studio over MCP
Studio documents an MCP server that agents use to create, start and stop local sites and to run WP-CLI commands and take screenshots. It runs over stdio through the Studio CLI. The manual configuration is a command of studio with the argument mcp, and the docs give one-line installs for two agents.
# checked on 15 Nov 2026 (wordpress.studio/docs/mcp-on-studio)
claude mcp add wordpress-studio -- studio mcp
codex mcp add wordpress-studio -- studio mcp
The docs name one tool, studio_instructions, which the agent calls before its first WordPress task so it loads Studio’s workflow rules on demand. They also note that Claude Code runs the Studio plugin with Node.js 22 or later on your PATH, and that you should start a new session after installing. Studio also reads instruction files and skills that already sit in the site directory, which fits the “short conventions file” habit above.
WordPress Playground for throwaway runs
Playground runs WordPress in a sandbox with temporary storage, so it suits “does this plugin even activate” checks. Its CLI can mount the project you are standing in.
# checked on 15 Nov 2026 (Playground CLI README)
npx @wp-playground/cli@latest server --auto-mount
npx @wp-playground/cli@latest server --blueprint=./my-blueprint.json
npx @wp-playground/cli@latest server --wp=6.8 --php=8.4
--auto-mount detects a plugin, theme, wp-content or WordPress directory. Without --wp and --php the CLI uses the latest WordPress and PHP 8.3, and it needs Node.js 20.18 or newer. A Blueprint is a JSON file that sets up the instance, so keep one in the repo and every agent run starts from the same state. Playground’s own docs say it is designed to work with AI coding agents and link a wp-playground agent skill guide.
The WordPress.org MCP server for plugin authors
If you plan to publish, WordPress.org documents its own MCP server (article dated 20 March 2026). It exposes three tools: Validate Readme, Get Plugin Status and Submit Plugin, plus guided prompts for preparing a submission, running Plugin Check and addressing review feedback. Setup is npx -y @wporg/mcp, which opens a browser to authorise an application password. The article is explicit that this is a workflow aid, not a replacement for the review process.
Exposing your own site through the MCP Adapter
The reverse direction is the official MCP Adapter package, which exposes WordPress abilities as MCP tools, resources and prompts. Abilities are private by default, so you must set meta.public or meta.mcp.public to true to expose one. Transports are STDIO through WP-CLI and HTTP at /wp-json/mcp/mcp-adapter-default-server. The repository documents migration guides for v0.3.0, v0.5.0 and v0.7.0, which tells you the API has moved before. Pin the version in anything you ship, and keep the exposed abilities narrow.
Which quality gates should AI-written WordPress code pass?
Every line the agent writes should pass the same three automated gates as human code: coding standards, static analysis and the WordPress.org plugin checks. Make them one command so the agent can run them itself and fix its own failures. An agent that can see a failing check will usually repair it in the next turn, and that loop is where most of the real time saving comes from.
WordPress Coding Standards (WPCS)
The WordPress Coding Standards repository documents a Composer install and says it needs PHP 7.2 or higher, which is a requirement of the tool, not of your plugin.
# checked on 15 Nov 2026
composer config allow-plugins.dealerdirect/phpcodesniffer-composer-installer true
composer require --dev wp-coding-standards/wpcs:"^3.0"
vendor/bin/phpcs -ps . --standard=WordPress
PHPStan with WordPress stubs
The szepeviktor/phpstan-wordpress extension adds WordPress function stubs and dynamic return types. It requires PHPStan 2.0 or higher. With phpstan/extension-installer there is no further setup; otherwise add the include line to phpstan.neon.
# checked on 15 Nov 2026
composer require --dev phpstan/phpstan szepeviktor/phpstan-wordpress phpstan/extension-installer
vendor/bin/phpstan analyse --level=5 src
Static analysis catches the typical agent habits of calling a method on a value that may be false or passing an array where a string is expected. Raise the level gradually, and do not accept a baseline file that hides new errors from the agent.
Plugin Check
Plugin Check is the official WordPress.org tool, at version 2.2.0 with 10,000+ active installs when we looked. It checks directory requirements and development practices across internationalisation, accessibility, performance and security. By default WP-CLI runs only the static checks.
# checked on 15 Nov 2026
wp plugin check acme-orders
# include runtime checks
wp plugin check acme-orders --require=./wp-content/plugins/plugin-check/cli.php
One command for all gates
{
  "scripts": {
    "lint": "phpcs -ps . --standard=WordPress",
    "stan": "phpstan analyse --level=5 src",
    "test": "phpunit",
    "check": ["@lint", "@stan", "@test"]
  }
}
Tell the agent in your instructions file: “Run composer check before you say you are done, and paste the output.” Reading the output yourself is still your job. An agent can summarise a failing run as a pass, so the log matters more than the claim. Our AI code review for WordPress plugins article covers using a model as a second reviewer on top of these tools, and running the standards check from inside the agent, through a tool or a plain shell command, keeps the loop short.
How do you test AI-generated code before it reaches a live site?
Test in layers: PHPUnit for logic, a local WordPress for behaviour, and a browser for anything a user sees. AI-written tests are a good start, but a test the same agent wrote for its own code can encode the same misunderstanding twice. Write or at least read the assertions yourself.
A local environment the agent can drive
@wordpress/env needs Docker with Compose v2, Node.js and git. It starts a site at http://localhost:8888 with the default login admin / password, and runs WP-CLI inside it.
# checked on 15 Nov 2026
npm i @wordpress/env --save-dev
npx wp-env start
npx wp-env run cli wp plugin list
npx wp-env run cli phpunit
The handbook describes the containers as mysql, wordpress, cli, composer and phpmyadmin, and uses wp-env run cli phpunit for PHPUnit. Because the default password is public knowledge, never expose this environment beyond your machine.
Tests that fail for the right reason
Ask for the test first, watch it fail, then ask for the code. This guards against an agent that writes a test and an implementation that agree with each other but not with the requirement.
<?php
// tests/test-slug-helper.php  (checked on 15 Nov 2026)
class Test_Slug_Helper extends WP_UnitTestCase {

	public function test_strips_html_and_lowercases() {
		$this->assertSame( 'hello-world', acme_orders_make_slug( '<b>Hello</b> World' ) );
	}

	public function test_empty_input_returns_fallback() {
		$this->assertSame( 'untitled', acme_orders_make_slug( '' ) );
	}
}
Then a short manual pass: install the plugin on a fresh site, run the main flow as an admin and as a logged-out visitor, and check the browser console. Agents rarely notice a JavaScript error that only appears on the front end. If the project has blocks, open one in the editor and confirm there is no “attempt recovery” warning.
Can AI review its own plugin for security problems?
It can find some problems and miss others, so use it as an extra reviewer, never as the only one. WordPress.org’s own guidance, in the MCP server article, says AI tools can introduce security vulnerabilities, license violations and unnecessary external service calls, and that you must review every change your AI assistant makes before submitting a plugin. We agree, and we apply it to our own work.
A short checklist catches most agent-written security faults. Ask the agent to produce the code, then check each item yourself.
- Every input is unslashed and sanitised on the way in, with a function that matches the data type.
- Every output is escaped for its context at the moment it is printed.
- Every state-changing request checks a nonce and a capability, not only one of them.
- Every database call with user data uses
$wpdb->prepare()or a core API. - No new outbound HTTP call, tracking or “phone home” code that you did not ask for.
- Function, class and option names carry your prefix.
<?php
// checked on 15 Nov 2026: a settings save handler that passes the checklist
function acme_orders_save_settings() {
	if ( ! current_user_can( 'manage_options' ) ) {
		wp_die( esc_html__( 'You do not have permission to do this.', 'acme-orders' ), 403 );
	}

	check_admin_referer( 'acme_orders_save', 'acme_orders_nonce' );

	$label = isset( $_POST['acme_label'] )
		? sanitize_text_field( wp_unslash( $_POST['acme_label'] ) )
		: '';

	update_option( 'acme_orders_label', $label );

	wp_safe_redirect( add_query_arg( 'updated', '1', wp_get_referer() ) );
	exit;
}
add_action( 'admin_post_acme_orders_save', 'acme_orders_save_settings' );
Agents are also exposed to a risk that human developers are not: text in the content they read can instruct them. If your agent reads issues, support tickets or pages from the web, treat that text as untrusted. The usual name for this risk is prompt injection, and it applies to any agent that reads untrusted text.
Security claims about specific plugins need a published advisory with an ID, affected versions and a date. We did not rely on any vulnerability report for this article, and you should not accept an agent’s unsourced claim that a plugin is or is not safe.
Common mistakes people report
These are recurring problems from official WordPress.org material and public issue trackers, paraphrased and dated. We checked each link on 15 November 2026.
- Unescaped output and unprefixed names. In a March 2023 WP Tavern report on the Plugin Review Team, a plugin built with ChatGPT failed review because variables and options were echoed without escaping in two places, and one function lacked the plugin prefix. Run Plugin Check and read the escaping findings yourself. Source: WP Tavern, 23 March 2023.
- Copied code and missing attribution. The same report says code in the directory must be GPL compatible, that a plugin containing code copied from another plugin was rejected five times, and that AI tools have been poor at crediting sources. Ask where a non-trivial snippet came from and check its licence.
- Shipping changes nobody read. The WordPress.org MCP article states you must review every change your AI assistant makes before submitting a plugin, and that you are responsible for all code in it. Source: Using the WordPress.org MCP Server, 20 March 2026.
- Skipping Plugin Check before submission. The same article calls running Plugin Check locally a prerequisite for submitting. Submitting first and fixing later costs review time. Source: Plugin Check on WordPress.org.
- Tool versions drifting apart. One Playground issue, opened 16 May 2026, reports that the
@wp-playground/mcpbridge accepted connections from playground.wordpress.net tabs but never registered a site, which the reporter suspects is a version mismatch between the hosted app and the package. When an MCP setup silently does nothing, check versions before you blame your prompt. Source: Playground issue 3651. The issue showed no maintainer response when we read it. - Copying a model ID from an old tutorial. Model lines retire. Read the current list and the retirement column before you hard-code an ID. Source: Anthropic models overview.
What does a practical AI workflow for WordPress look like?
This is the order we would follow on a new plugin. It works with any agent that can run shell commands, and it keeps a human at each decision point. For a worked example with one specific agent, see our Claude Code workflow for WordPress.
- Write the brief. One page: what the plugin does, who uses it, what it must never do, minimum PHP and WordPress versions, text domain and prefix.
- Scaffold. Use
wp scaffold pluginorcreate-block, run the quality gates once on the empty project, and commit. - Plan with the agent, decide yourself. Ask for a file layout and data model, challenge it, and write the agreed plan into the instructions file.
- Build in small slices. One feature per prompt, one commit per slice, tests alongside.
- Run the gates after every slice.
composer check, thenwp plugin check, with the output pasted back. - Run it somewhere real. Start it in Playground or
wp-env, walk the flows in a browser, and test at 390px width if there is any front-end output. - Review the diff like a stranger wrote it. Security checklist, licence check, unneeded dependencies, anything that makes an outbound request.
- Document and release. Let the agent draft the readme, then validate it. For publishing, the WordPress.org MCP tools can check the readme and track review status.
Themes follow the same loop with different gates. Validate theme.json by loading the theme in the editor on a test site, and do a visual pass through every template. Block themes reward this approach because their structure is declarative, so an agent has less room to invent behaviour.
Should an agent ever work directly on a live WordPress site?
Not by default. Let agents work on a local site, a Playground instance or a staging copy, then deploy through your normal process. If you expose a production site through the MCP Adapter, expose only the specific abilities you need, make each one check capabilities, and log what gets called. The adapter makes abilities private by default for a reason, so keep it that way unless you have a written case for each one you open.
Give an agent the narrowest credentials that do the job. For WordPress.org, the MCP server uses an application password, only one exists per account, it is shown once, and you can revoke it from your profiles.wordpress.org settings. Treat it like any other secret, and keep it out of the repository and out of the prompt.
What do AI agents still get wrong in WordPress work?
They get the long tail wrong. A model has seen a great deal of common WordPress code and much less of your hosting quirks, your theme’s overrides or the way a three-year-old plugin on your site filters the same hook. Expect these weak spots and test for them directly.
- Version awareness. The agent may use a function that exists only in a newer WordPress, or a pattern the handbook has since replaced. Check against developer.wordpress.org and set your minimum versions in the instructions file.
- Plugin interactions. It does not know what else is active. Test with the plugins your target sites actually run.
- Performance. A query that is fine on 20 posts can fall over on 20,000. Seed a large dataset and profile before release.
- Scope creep. Agents add options, abstractions and settings pages nobody asked for. Reject them in review; every extra option is code you maintain.
- Confident wrong answers. An agent will describe a hook or function that does not exist. If you cannot find it in the reference, assume it is invented.
There is also a maintenance side effect: fast generation produces fast accumulation. Managing it comes down to habits: smaller diffs and passing gates keep the debt visible.
Frequently asked questions
Which Claude model should I use for WordPress plugin development?
Start with Claude Opus 5.5 for agentic coding, which is where Anthropic points most workloads as of 15 November 2026. Move up to Fable 5.2 if your own tests show Opus falling short, and use Sonnet 5.5 or Haiku 5.5 for faster or cheaper chores. Run the same task on two models in your own repository before you commit to one.
Is Claude 3.5 Sonnet still available?
It is not on Anthropic’s current models list as of our check on 15 November 2026. Use the models overview page for the current IDs and retirement commitments, and avoid hard-coding an ID from an old tutorial.
Can AI generate a whole WordPress theme or plugin?
It can generate a working first draft of many plugins, especially small ones built on a scaffold. Whether that draft is fit to ship depends on the review, tests and security checks you apply afterwards. Treat the draft as untrusted code from a fast junior developer.
Does AI-generated code pass WordPress.org plugin review?
The Plugin Review Team applies the same rules to every submission. According to the WordPress.org MCP article, you are responsible for all code in your plugin however it was produced, and the guidelines apply in full. Running Plugin Check locally first is a stated prerequisite.
Is it safe to let an agent run WP-CLI on my site?
On a local or staging site, yes, with the usual backups. On production, only with narrow permissions, logging and an explicit list of commands. WP-CLI can delete content and change options, and an agent acts on whatever instructions it reads.
Do I need WordPress Studio, Playground or wp-env?
You need one reliable place to run the code. Studio suits a desktop workflow with an agent that supports MCP. Playground suits quick disposable checks. wp-env suits repeatable test runs and CI-style work because it uses Docker and a fixed configuration. Pick one and write its start command in your instructions file.
Where can I compare AI coding tools?
We keep the tool comparisons in two other articles so this one can stay on workflow. See our best AI tools for WordPress development and our Claude Code, Copilot and Cursor compared.
No comments yet