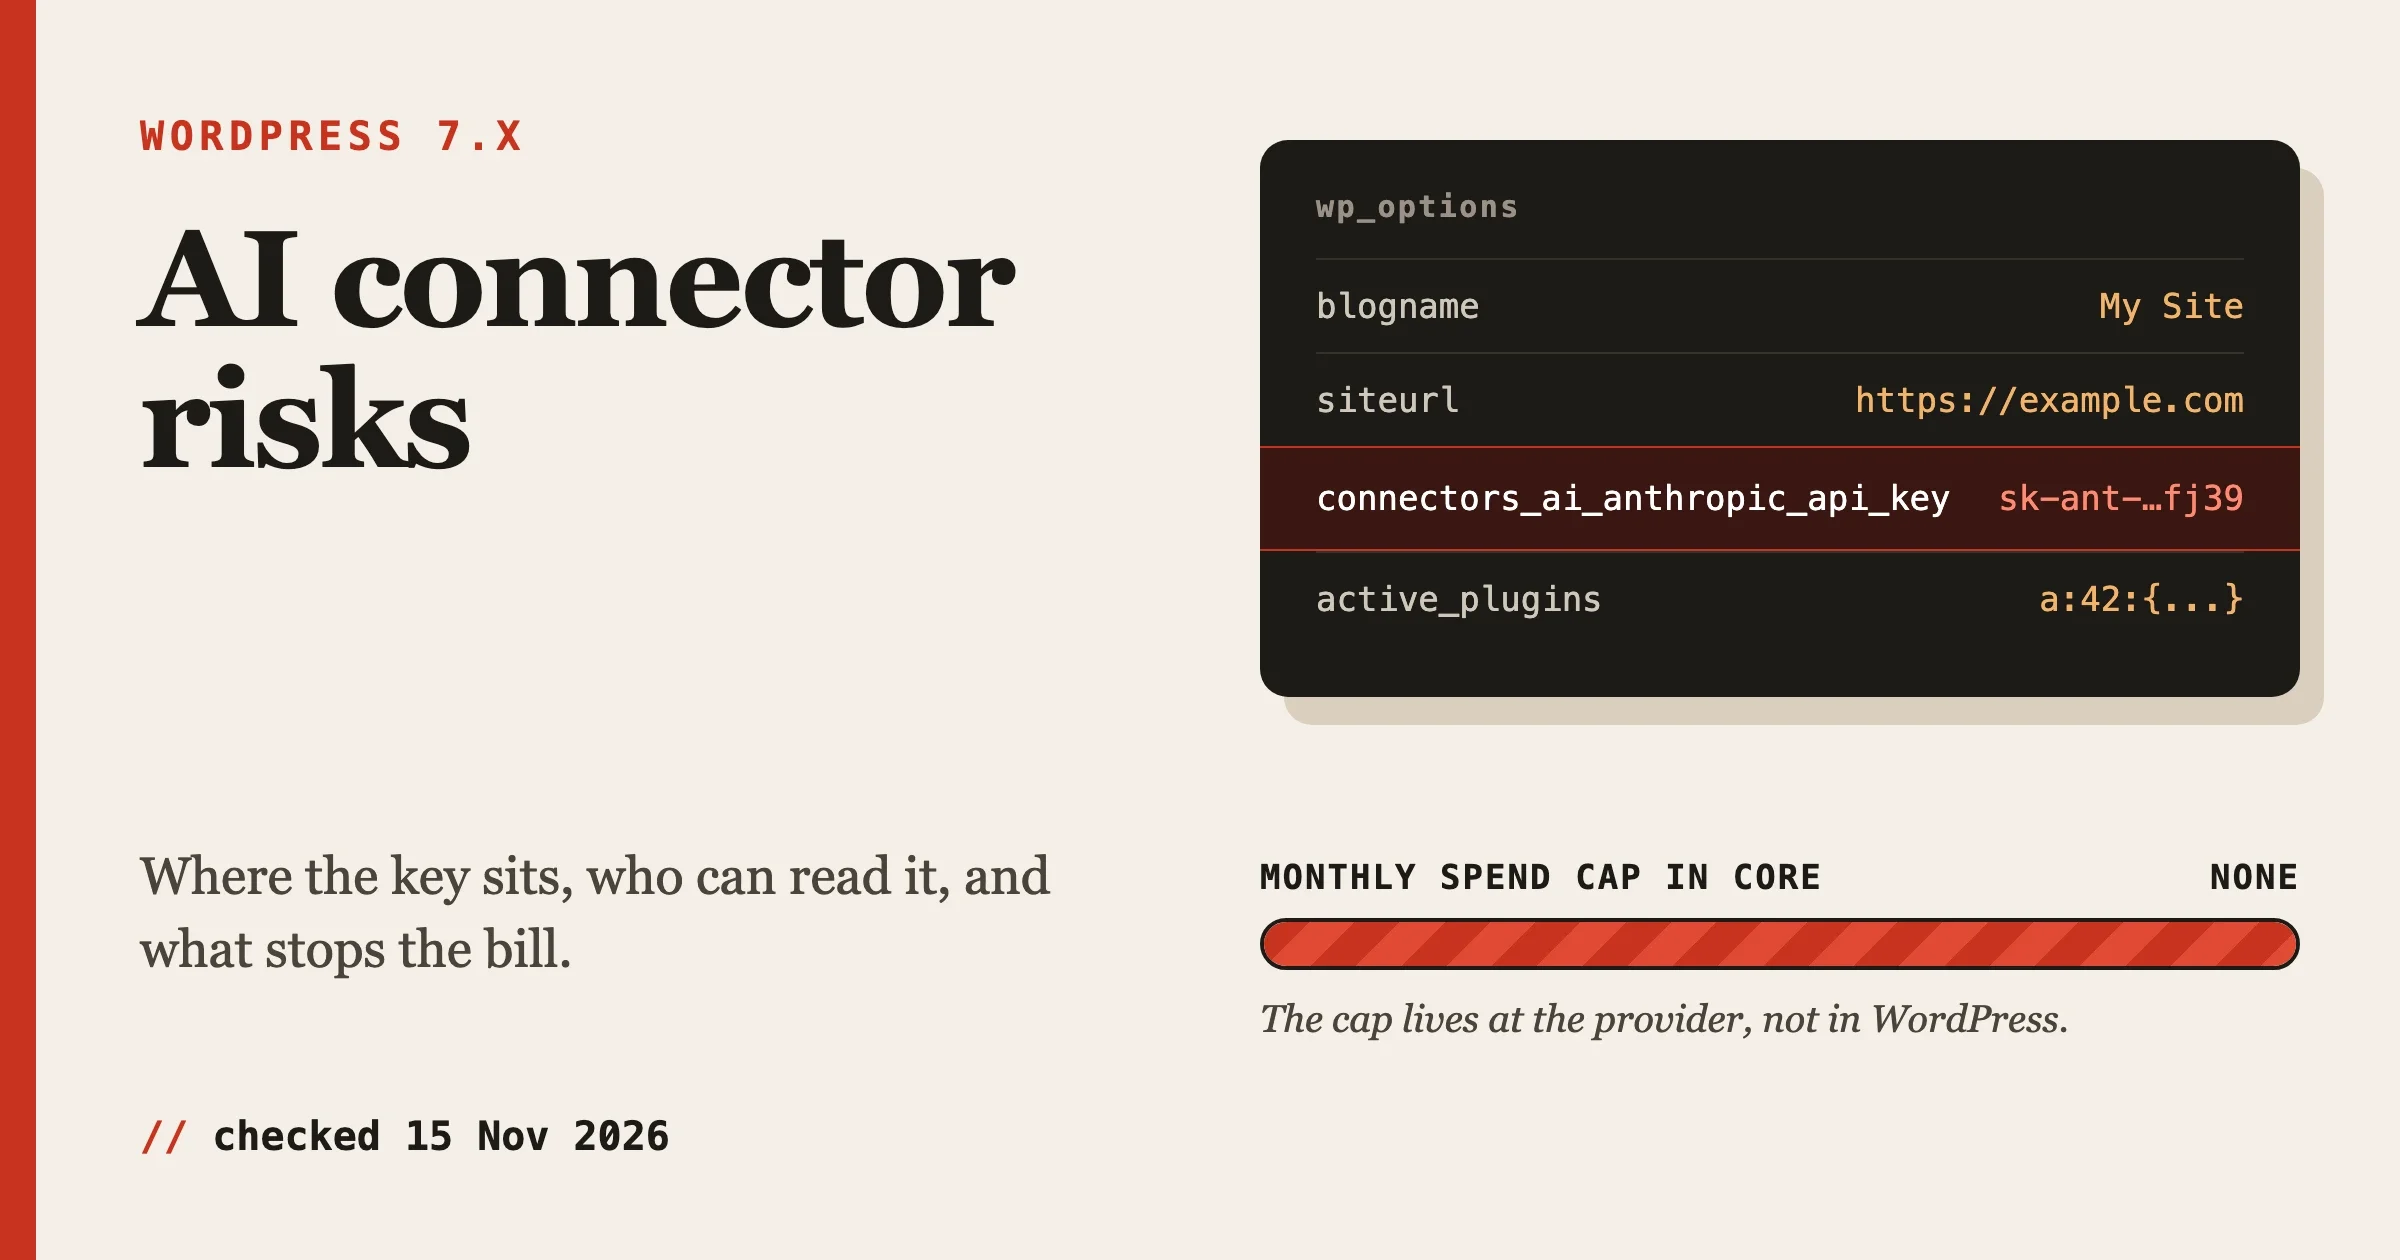
The main risk of WordPress AI connectors is simple: a paid credential for Anthropic, Google or OpenAI now sits on your site, and any code that runs on the site can use it. Core stores the key as a plain option (unless you move it to a constant or an environment variable), masks it only on the Settings > Connectors screen and in REST responses, and puts no spending cap, rate limit or per-plugin permission in front of it. The privacy risk is the other half: every prompt a plugin builds goes to a third party. Neither risk is a reason to avoid AI. Both are cheap to contain once you know where they sit.
We rewrote this article on 15 Nov 2026. The first version, written while WordPress 7.0 was in release candidate, described connectors as a registry of callable capabilities. That was wrong: the Connectors API stores connections to outside services, mostly AI provider keys. We re-read the WordPress 7.0, 7.1 and 7.1.4 source, the official Connectors dev note and its comments, provider documentation, the wordpress.org plugin API and four published advisories, and every figure below carries a checked date. The how-to side (registering a connector in code) lives in our companion piece, the WordPress 7.0 Connectors API guide for plugin developers. This article is about what can go wrong and what to do about it. WordPress 7.0 “Armstrong” shipped on 20 May 2026, 7.1 “Mary Lou” on 19 Aug 2026, and the current stable release is 7.1.4.
What are the risks of WordPress AI connectors?
There are seven, and each one has a cheap fix. This table is the whole article in one screen; the sections after it give the evidence.
Risk | Why it exists | Cheapest fix |
|---|---|---|
Any plugin can read the key | A core contributor confirmed in the dev note comments that the saved key is a site setting, so every plugin can access it, and a key in a constant or environment variable has the same exposure to installed code | Install fewer plugins; turn on the AI plugin’s Connector Approval experiment if you run it |
The key sits in the database | Core does not encrypt it, so it travels in every backup, staging copy and SQL dump | Move it to a constant or environment variable and delete the saved copy |
No spending cap in core | We found no quota, cost counter or capability check in the AI Client files; the only gates are the | Hard spend limit at the provider, one key per site |
Visitors can trigger paid requests | Some plugin features run on visitor input; the WordPress AI plugin’s Comment Moderation experiment checks every new comment, including comments from visitors | Know which features run automatically; gate prompts by capability |
Prompts leave your server | Whatever a plugin puts in a prompt is sent to the provider, which keeps it for a period and acts as your data processor | Check the provider terms and your privacy notice before you switch features on |
Plugins that leak keys | Four published advisories (2025 and 2026) cover AI plugins that exposed a stored provider key or token | Update fast, rotate any key a vulnerable plugin held |
Browser autofill showed the key | On 7.0 the key field could offer saved keys in the browser’s autofill dropdown; fixed in Gutenberg with an autocomplete attribute | Update WordPress and Gutenberg; do not save keys in shared browsers |
Checked on 15 Nov 2026 against WordPress core 7.1.4, the Connectors dev note and the sources listed at the end.
Where does WordPress store my AI API key, and who can read it?
In the wp_options table, unless you set the key somewhere else. For the three built-in providers the option names are connectors_ai_anthropic_api_key, connectors_ai_openai_api_key and connectors_ai_google_api_key. Core checks three places in a fixed order: an environment variable, then a PHP constant, then that database option. The provider constants follow one pattern: ANTHROPIC_API_KEY, OPENAI_API_KEY and GOOGLE_API_KEY.
Who can see it depends on the path:
- Through the admin screen. Settings > Connectors needs the
manage_optionscapability, so on a single site only administrators open it. The page data tells the browser where the key comes from (environment, constant or database) and whether the provider is connected. It does not include the key. - Through the REST API. The key option is registered with REST visibility, so it appears in
/wp/v2/settingsfor users who can manage options. Core masks it there: bullet characters plus the last four characters, capped at sixteen bullets. - Through PHP. Any plugin, theme or mu-plugin can call
get_option()and receive the raw key. The mask is a filter on that one REST route, so it protects the screen and nothing else. - Through your backups. A database export, a staging clone or a SQL dump emailed to a freelancer contains the key in clear text.
The official dev note says it plainly: keys stored in the database are not encrypted but are masked in the interface, and encryption is being explored in Trac ticket 64789. In the comments, a reader asked whether a key is scoped to one plugin. A core contributor answered that it is a site setting, so every plugin can access it, and that a key in an environment variable or constant is just as reachable by the third-party code you install. We found no encryption of connector keys in the 7.0, 7.1 or 7.1.4 source.
One more behaviour matters for support. When you save a key for an AI provider, core sends it to the provider through the AI Client to test it. If the provider rejects it, core empties the option and shows a generic failure. A key that works is not re-checked later, so a revoked key keeps sitting in the database until a request fails.
How do I check what my site holds?
List the connector options without printing their values. This shows which providers have a saved key and whether the option is autoloaded.
# Checked on 15 Nov 2026 against WordPress 7.1.4. Lists names only, never values.
wp option list --search='connectors_*' --fields=option_name,autoload
An empty result means no key is saved in the database. It does not prove none is configured: a key in wp-config.php or the server environment will not appear here. The Settings > Connectors card shows the source for each one.
Can a plugin or a site visitor run up my AI bill?
Yes, and core will not stop it. Any code that calls wp_ai_client_prompt() spends the connected key. We read the AI Client files in 7.1.4 (the function file and the prompt builder) and found no capability check, no quota and no cost counter. The builder honours two switches: wp_supports_ai, which turns AI off for a request, and wp_ai_client_prevent_prompt, a filter that receives a read-only clone of the builder and can block a prompt before it runs. Nothing is blocked unless you or a plugin adds that filter.
That matters most for features that run without a human click. The WordPress AI plugin (version 1.5.0, 60,000+ active installs, tested up to 7.1.4, checked on the wordpress.org API on 15 Nov 2026) is opt-in: nothing is on after activation. Its readme is candid about the rest. Most experiments send a request only when you click a button, but some run on their own, and Comment Moderation, for example, checks every new comment, including comments from site visitors, by default. A spam run against a blog with that experiment on is a run against your AI bill.
The AI plugin also ships two experiments aimed at exactly this risk. Connector Approval requires an administrator to approve other plugins and themes before they can use your configured connectors. AI Request Logging records requests with short previews of prompts and responses, which helps you see who spends what. Both are experiments that may change in any release, so test them on staging first.
What spend limit should I set at the provider?
Set a hard limit on the provider side, because it is the only cap that holds whatever your plugins do. Use one key per site, so a leak on one site does not drain another.
Provider | What the docs say (checked 15 Nov 2026) | What to do |
|---|---|---|
Anthropic | Each usage tier has a monthly spend cap: Start $500, Build $1,000, Scale $200,000. You can set your own lower limit in the Console, and set limits per workspace. You cannot set spend limits on the default workspace. At a limit you set, requests return HTTP 400 | Create a workspace for the site, set a monthly limit well below the tier cap, create the key inside that workspace |
OpenAI | Spend alerts only send a notification and traffic continues. A hard limit is a separate switch in Project settings, Limits, Spend: turn on “Enforce a hard limit”. Reaching a project hard limit returns a 429 with the | One project per site, monthly limit set, hard limit enforced, alert set at 50 percent |
We did not verify Google’s limit behaviour for this article | Check your Google Cloud billing budget and quota settings; budgets alone may only alert, so confirm a hard stop |
How do I stop visitors and low-privilege users from triggering prompts?
Add the prevent filter in a must-use plugin and allow prompts only for people who can edit posts. This blocks anonymous visitors and subscribers whatever plugin made the call.
<?php
/**
 * Plugin Name: Gate AI prompts
 * Description: Lets only users who can edit posts (and WP-CLI) run AI prompts.
 */

// Checked on 15 Nov 2026 against WordPress 7.1.4 core source.
add_filter(
	'wp_ai_client_prevent_prompt',
	static function ( bool $prevent ): bool {
		if ( $prevent ) {
			return true;
		}

		if ( defined( 'WP_CLI' ) && WP_CLI ) {
			return false;
		}

		// Anonymous visitors and subscribers fail this check.
		// Scheduled jobs also fail it; add wp_doing_cron() here if you need them.
		return ! current_user_can( 'edit_posts' );
	}
);
Test it on staging: trigger an AI feature as a subscriber and confirm it fails with a prompt_prevented error (the builder returns that code with a 503 status when a filter blocks a prompt). Cron-driven features stop until you allow that context.
What data does the AI connector send to the provider, and is that GDPR safe?
It sends whatever the calling plugin puts in the prompt. Core adds nothing and filters nothing. A summarise button sends the post text. A comment moderation experiment sends each comment. A support chatbot sends the visitor’s message, and possibly their name or order details if the developer included them. The connector only carries the key and the request.
Providers state their retention rules in public documents. As checked on 15 Nov 2026:
- OpenAI says abuse monitoring logs are retained for up to 30 days by default, and that data sent to the API is not used to train its models unless you opt in. Zero Data Retention is an approval-based control and does not cover every endpoint.
- Anthropic says it automatically deletes inputs and outputs from its backend within 30 days of receipt or generation, with exceptions for services with longer retention under your control, a separate agreement such as zero data retention, usage-policy enforcement and legal compliance. Its Commercial Terms incorporate a Data Processing Addendum.
For a site that handles personal data of people in the EU or UK, the practical steps are the same as for any processor. Sign or accept the provider’s data processing agreement, list the provider in your privacy notice, decide which features may receive personal data, and keep visitor-facing features off until you have done that. Our piece on GDPR and WordPress AI plugins walks through the legal side in more depth. We are not lawyers, and this is not legal advice.
- Keep logs short. AI Request Logging stores prompt and response previews in your own database. That log is personal data too if prompts contain it, so it needs a retention period.
- Keep sensitive data out of prompts. Strip names, emails and order numbers before the call unless the feature needs them.
- Consider a local model for sensitive work. A model on your own hardware sends nothing to a third party. We cover that setup in running Ollama and LM Studio with WordPress.
Have WordPress AI plugins actually leaked API keys?
Yes. None of the four published advisories below is a flaw in core’s Connectors code. All four are in AI plugins that stored a provider key or token and exposed it to someone who should not have read it. We checked each ID on cve.org and NVD on 15 Nov 2026.
ID | Plugin | What was exposed, and to whom | Affected, fixed | Published |
|---|---|---|---|---|
CVE-2025-11749 | AI Engine | A bearer token for its MCP endpoint, readable by unauthenticated visitors when the “No-Auth URL” option is on; NVD scores it 9.8 Critical because the token allowed creating an administrator account | Up to and including 3.1.3 | 5 Nov 2025 |
CVE-2026-1336 | AI ChatBot with ChatGPT and Content Generator by AYS | The stored ChatGPT API key could be viewed, changed or deleted by unauthenticated attackers (CVSS 5.3) | Up to and including 2.7.5, fully fixed in 2.7.6 | 3 Mar 2026 |
CVE-2026-6639 | AI Copilot - Content Generator (AIWU) | Stored OpenAI API keys, prompts and model settings, readable by unauthenticated attackers who enumerated task IDs (CVSS 7.5) | Up to and including 1.4.6; check the plugin page for the fixed version | 5 Aug 2026 |
CVE-2026-16954 | AI Engine | Third-party API keys and tokens printed in admin page script data, so Editor-role users could read keys meant for administrators (CVSS 6.5) | Before 3.6.4, fixed in 3.6.4 | 6 Aug 2026 |
Three of the four needed no login at all; the fourth let an Editor read keys meant for administrators. Updating a plugin closes the hole but does not cancel a key someone already copied, so after any advisory like these, rotate the key at the provider.
Security researchers expected this. Patchstack’s founder wrote on X shortly after the 7.0 release that WordPress 7.0 combined with plugin vulnerabilities means “free AI tokens” for attackers, as Search Engine Journal reported on 22 May 2026. That article describes a forecast, not a confirmed campaign, and we did not find a report of a mass theft of connector keys while researching this piece.
What was the browser autofill problem?
On WordPress 7.0, a browser could save the key you typed into the Connectors screen and offer it in its autofill dropdown, so anyone using the same browser profile could see it. The report is Gutenberg issue 78945 (closed 4 Jun 2026) and Trac ticket 65303. The fix merged in Gutenberg 23.4 added an autocomplete attribute to the field. A proposal to turn the field into a password input was closed in July after reviewers preferred the attribute. If you manage keys from a shared computer or a browser with sync on, clear saved form data after you paste a key, or set the key as a constant and never type it into the screen.
How do I reduce the risk of WordPress AI connectors?
Work down this list. Steps 1 and 2 take five minutes and remove most of the exposure.
- Decide if the site needs AI at all. If not, define
WP_AI_SUPPORTas false inwp-config.php. Core then skips the built-in AI provider connectors and refuses to register any connector of typeai_provider. - Keep keys out of the database. Set them as constants or environment variables. Core checks those first, so they win over a saved option.
- Use one key per site with a hard spend limit. See the provider table above.
- Gate prompts by capability. Use the must-use plugin from the cost section.
- Audit who can use the key. List active plugins that call AI features. Remove the ones you do not use. If you run the AI plugin, test Connector Approval on staging.
- Rotate on a schedule and after every incident. Rotation matters most after an advisory, a salt change, a staff departure or a database copy leaves your control.
- Keep WordPress, Gutenberg and AI plugins current. Update within days of an advisory, then rotate the key.
Our WordPress security hardening checklist covers the general controls (administrator count, file editing, two-factor login) that also protect these keys.
<?php
// wp-config.php. Checked on 15 Nov 2026 against WordPress 7.1.4 core source.
// Core reads the environment variable first, then this constant, then the database.
// Use the line for your provider only, and paste the key from your password manager.
define( 'ANTHROPIC_API_KEY', 'paste-key-here' );
// define( 'OPENAI_API_KEY', 'paste-key-here' );
// define( 'GOOGLE_API_KEY', 'paste-key-here' );

// Or turn AI off for this site entirely:
// define( 'WP_AI_SUPPORT', false );
A constant in wp-config.php still lives on disk and in your repository if you commit that file. Keep it out of version control, or load the value from the server environment instead. The constant also remains readable by every plugin, as noted above. It removes the database copy, not the trust problem.
How do I rotate a key that was saved in the database?
Replace it at the provider first, so the old key is dead before anything else. Then move the new key out of the database.
# Checked on 15 Nov 2026 against WordPress 7.1.4 and WP-CLI.
# 1. In the provider console: create a new key, then revoke the old one.
# 2. Set the new key as a constant (this puts it in your shell history, so
#    clear the history, or edit wp-config.php by hand instead).
wp config set ANTHROPIC_API_KEY 'paste-new-key' --type=constant

# 3. Delete the saved copy so no old key stays in the database.
wp option delete connectors_ai_anthropic_api_key
Deleting the option does not remove the key from earlier backups and staging copies. That is why revoking at the provider comes first: a revoked key is harmless in an old dump.
Should I turn AI connectors off?
Turn them off if nobody on the site uses an AI feature. Leave them on, with the controls above, if someone does. The decision is about the site, not about AI in general.
Your situation | What we would do | Why |
|---|---|---|
Brochure site, no AI features in use | Set | Removes the built-in connectors and the credential from the site |
Editors use AI for drafts, alt text or summaries | Key as a constant, hard provider limit, prompt gate for | Staff use is the real need; visitors never need to spend your tokens |
Visitor-facing AI (chatbot, comment moderation) | Dedicated key and project, low hard limit, logging on, privacy notice updated | The bill and the personal data both depend on strangers |
Agency managing many client sites | One key per client site, billed or capped per client | A leak or a bill on one client stays on that client |
Sensitive or regulated content | Local model, or no AI on that site | Nothing leaves your servers |
Will the WordPress 7.2 Secrets API fix key storage?
Maybe in part, and not yet. WordPress 7.2 is scheduled for 8 Dec 2026. The development tree contains a Secrets API (functions such as wp_set_secret() and wp_get_secret()) that stores credentials encrypted. The dev note of 11 Nov 2026 records objections from senior contributors, and we cannot tell you it will ship in 7.2. When we diffed the connector code between 7.1 and the development tree on 15 Nov 2026, it did not call the Secrets API, so connector keys are still plain options there.
The WordPress AI plugin has moved its Key Encryption experiment onto the Secrets API feature plugin, per its 1.5.0 changelog (29 Oct 2026). The readme says it encrypts AI provider keys stored in your database, and that disabling the experiment or deactivating the plugin restores plaintext keys. One reported failure shows the trade-off: in AI plugin issue 1185 (fixed in 1.5.0), changing the site’s login keys and salts, for example with a salt shuffle or a security plugin’s “log out everyone” button, left the stored key undecryptable and caused fatal errors on every request. So if you try encryption, back up first and keep a copy of the key in your password manager.
For the full 7.2 picture see our Secrets API guide, and for the registry details see the Connectors API guide. Until the final 7.2 behaviour is confirmed, do not build a plan that depends on it.
Common mistakes people report
These come from public issues, the dev note thread and plugin changelogs. Each is paraphrased, with the state we saw on 15 Nov 2026.
- Assuming the key is private to one plugin. It is not. In the Connectors dev note comments (24 Mar 2026), a core contributor said the saved key is a site setting, so every plugin can access it.
- Typing the key into a shared browser. WordPress 7.0 let browsers store the key and show it in autofill (Gutenberg issue 78945, closed 4 Jun 2026). Update, and clear form data on shared machines.
- Trusting the mask. The bullets in Settings > Connectors and REST output protect the screen. The raw key is still in the database, in backups and in every PHP call to
get_option(). - Blaming the key when the key is fine. AI plugin issue 1069 (closed 29 Sep 2026) showed the Connector Approval experiment blocking core’s own key check, so a valid key looked wrong with a generic “not possible to connect” message. If a good key keeps failing, check what intercepts the provider request, and look under Tools for a pending approval.
- Turning on encryption without a backup. AI plugin issue 1185 (closed 16 Oct 2026) showed a salt change breaking a site that used the Key Encryption experiment. Back up before you try it, and keep the key elsewhere.
- Forgetting that updating is not rotating. After any of the advisories above, the fixed version stops new leaks but does not cancel a key someone already read. Revoke and replace it at the provider.
Frequently asked questions
Is the WordPress AI API key encrypted?
Not by core. Connector keys are saved as plain options and masked in the Connectors screen and REST output. Keys set as constants or environment variables never touch the database. The AI plugin’s Key Encryption experiment can encrypt stored keys, and the 7.2 Secrets API may change this, but neither is part of core connectors today.
Can any plugin use my AI connector key?
Yes. A core contributor confirmed that the key is a site setting that every plugin can access, and the same holds for a key in a constant or environment variable. The AI plugin’s Connector Approval experiment adds an approval step if you run that plugin.
How do I cap what a leaked AI key can cost?
Cap it at the provider. Use a project or workspace per site with a monthly spend limit, and on OpenAI turn on the hard limit switch, because alerts alone do not stop traffic. Core has no cap of its own.
What should I do if an AI plugin on my site has a vulnerability?
Update the plugin, revoke the provider key it held, create a new key with a spend limit, and check the provider’s usage page for requests you did not make. Then delete any saved copy of the old key from the database.
Sources, checked on 15 Nov 2026
- WordPress core source at the 7.0.0 and 7.1.4 tags:
connectors.php,ai-client.php, the AI Client prompt builder andoptions-connectors.php - Introducing the Connectors API in WordPress 7.0, make.wordpress.org, 18 Mar 2026, including the comments
- The WordPress AI plugin readme and changelog, via the wordpress.org plugin API
- Gutenberg pull request 78946 and issues 78945 and 78965; AI plugin issues 1069 and 1185 on GitHub
- Anthropic rate and spend limits and Anthropic data retention documentation
- OpenAI spend limits and OpenAI data controls documentation
- Advisories on cve.org and NVD: CVE-2025-11749, CVE-2026-1336, CVE-2026-6639, CVE-2026-16954
- WordPress 7.0 faces security concerns over AI API keys, Search Engine Journal, 22 May 2026
No comments yet